Key Takeaways
- The best HIPAA compliance software in 2026 includes Scytale, Drata, Vanta, Sprinto, Secureframe, Compliancy Group, Abyde, Accountable HQ, Rhythm360, and ComplyJet, offering solutions for healthcare organizations, medical practices, and healthtech startups.
- AI-powered HIPAA compliance tools streamline security risk assessments, automated evidence collection, continuous monitoring, employee training, vendor management, and audit readiness while strengthening patient data protection.
- Choosing the right HIPAA compliance software requires comparing pricing, regulatory coverage, integrations, ease of use, scalability, and security features to ensure long-term compliance management and operational efficiency.
HIPAA compliance software helps healthcare organizations protect patient data, manage security risks, and maintain regulatory readiness. The best HIPAA compliance software in 2026 includes Scytale, Drata, Vanta, Sprinto, Secureframe, Compliancy Group, Abyde, Accountable HQ, Rhythm360, and ComplyJet, with capabilities spanning automated risk assessments, employee training, compliance monitoring, and audit preparation.
Healthcare organizations face growing challenges in protecting sensitive patient information, managing cybersecurity risks, and meeting increasingly complex regulatory requirements. As electronic health records (EHRs), cloud-based healthcare applications, telehealth platforms, and artificial intelligence become more widely adopted, maintaining compliance with the Health Insurance Portability and Accountability Act (HIPAA) has become a critical priority for healthcare providers, medical practices, healthtech startups, and business associates.

The best HIPAA compliance software in 2026 helps organizations streamline regulatory compliance through automated security risk assessments, continuous monitoring, policy management, employee training, vendor risk assessments, and centralized audit documentation. Leading platforms such as Scytale, Drata, Vanta, Sprinto, Secureframe, Compliancy Group, Abyde, Accountable HQ, and ComplyJet offer different approaches to managing compliance obligations, while specialized healthcare platforms such as Rhythm360 incorporate HIPAA-related security capabilities into clinical workflows.
HIPAA compliance extends beyond implementing basic cybersecurity measures. Organizations subject to HIPAA must address applicable requirements under the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule. These obligations include protecting electronic protected health information (ePHI), conducting security risk analyses, implementing appropriate administrative, physical, and technical safeguards, managing Business Associate Agreements (BAAs), and maintaining required compliance documentation.

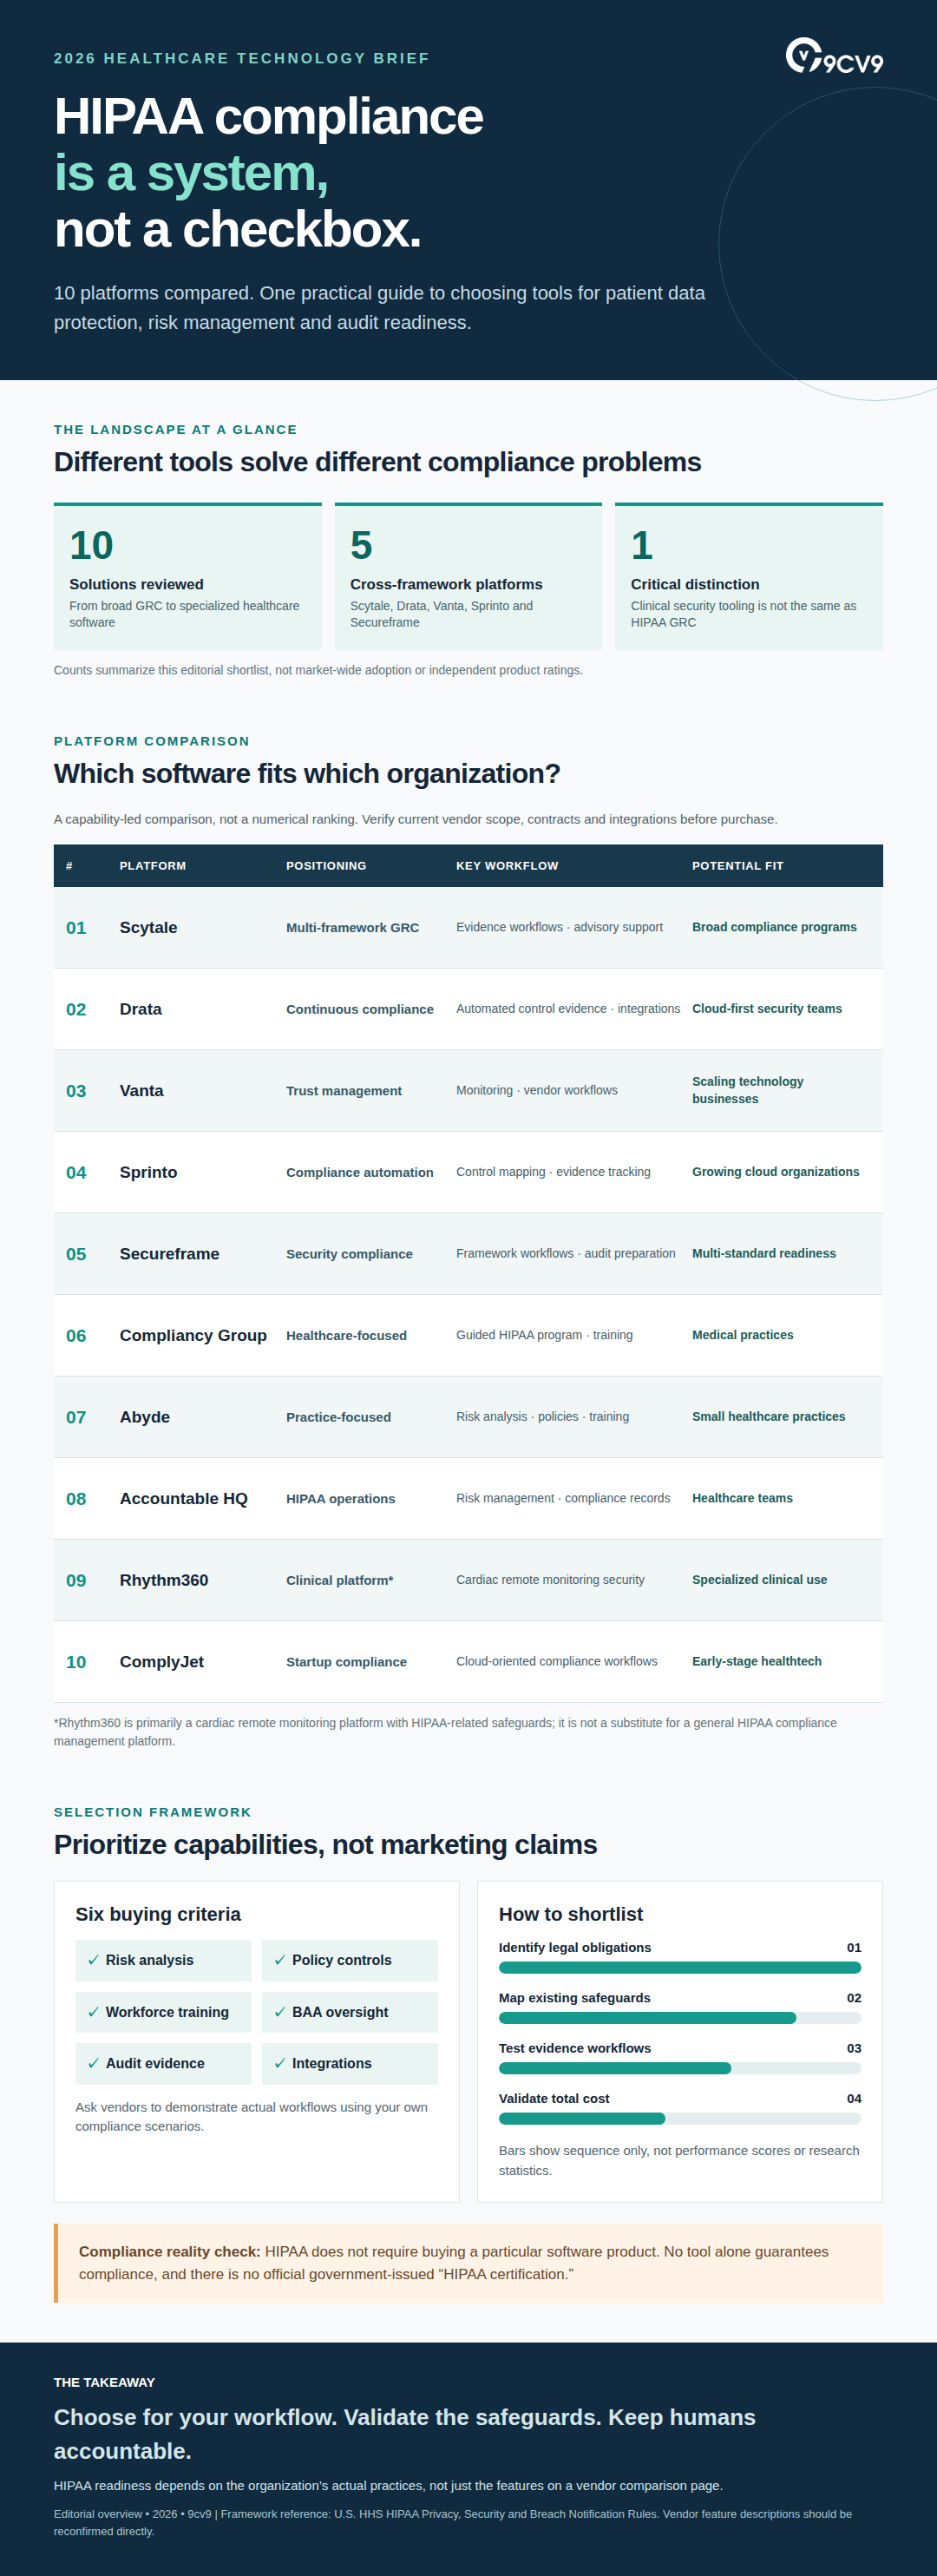
In 2026, artificial intelligence and compliance automation are reshaping how healthcare organizations approach these responsibilities. Modern HIPAA compliance management platforms increasingly incorporate automated evidence collection, AI-assisted policy development, security control monitoring, integration with cloud infrastructure, and proactive risk identification. These capabilities can reduce manual administrative work, improve visibility into security gaps, and support more consistent compliance management. However, software alone cannot guarantee HIPAA compliance or replace organizational accountability.
Choosing the right HIPAA compliance solution requires careful consideration of several factors, including regulatory coverage, ease of implementation, pricing, scalability, integration capabilities, customer support, and compatibility with existing healthcare technology systems. Small medical and dental practices may prioritize affordable, healthcare-specific compliance software with guided training and documentation, while larger healthcare organizations and technology companies may require enterprise-grade governance, risk, and compliance (GRC) platforms supporting multiple frameworks such as SOC 2, ISO 27001, and HIPAA.
This comprehensive guide explores the top 10 best HIPAA compliance software solutions in the world in 2026, comparing their key features, compliance automation capabilities, security tools, pricing considerations, advantages, limitations, and suitability for different healthcare environments. Whether an organization is establishing its first HIPAA compliance program, replacing manual compliance processes, or strengthening an existing security framework, this comparison provides practical insights to help identify the most appropriate software for protecting patient information and maintaining long-term regulatory readiness.
Before we venture further into this article, we would like to share who we are and what we do.
About 9cv9
9cv9 is a business tech startup based in Singapore and Asia, with a strong presence all over the world.
With over ten years of startup and business experience, and being highly involved in connecting with thousands of companies and startups, the 9cv9 team has listed some of the top and best companies/tools in this review.
If you like to get your company listed in our top B2B software reviews, check out our world-class 9cv9 Media and PR service and pricing plans here.
Top 10 Best HIPAA Compliance Software To Know in 2026
1. Scytale
Scytale is an AI-powered governance, risk, and compliance (GRC) platform designed to help healthcare technology companies, digital health providers, and organizations handling protected health information (PHI) streamline HIPAA compliance management. By combining automated evidence collection, continuous security monitoring, and dedicated compliance specialists, Scytale provides a centralized environment for managing regulatory requirements and maintaining audit readiness.
Unlike traditional HIPAA compliance software that relies heavily on manual checklists and periodic assessments, Scytale integrates directly with cloud infrastructure, identity management systems, and enterprise applications to monitor security controls continuously. Its multi-framework architecture also enables organizations to coordinate HIPAA requirements alongside SOC 2, ISO 27001, GDPR, PCI DSS, and other security standards.
Core HIPAA Compliance Features and Capabilities
Scytale supports HIPAA compliance through automated risk assessments, policy management, workforce training, vendor oversight, and ongoing security control monitoring.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Risk Assessment | Identifies potential risks to electronic protected health information | Supports HIPAA Security Rule risk analysis |
| Automated Evidence Collection | Collects compliance evidence from connected applications | Reduces manual documentation |
| Continuous Control Monitoring | Evaluates security controls and identifies configuration changes | Improves visibility into security weaknesses |
| HIPAA Self-Assessment | Organizes internal compliance reviews | Supports compliance gap identification |
| Policy Management | Provides customizable security and privacy policy templates | Standardizes compliance documentation |
| Workforce Training | Supports HIPAA security awareness activities | Improves employee understanding of security responsibilities |
| Vendor Risk Management | Tracks third-party security assessments | Strengthens business associate oversight |
| Access Reviews | Monitors user access and permissions | Supports access governance |
| Compliance Dashboard | Centralizes controls, evidence, and remediation tasks | Improves compliance reporting |
AI Automation and Intelligent Compliance Management
Scytale incorporates agentic AI capabilities to automate repetitive governance and compliance activities. Its AI-driven workflows assist with evidence evaluation, security questionnaire responses, compliance task management, and risk identification.
The platform can identify security configuration issues, monitor access control changes, and highlight missing or ineffective safeguards based on information available through connected systems.
Its AI-powered security questionnaire functionality also helps organizations prepare responses to enterprise customer assessments using existing compliance documentation.
| AI Capability | Application | Operational Value |
|---|---|---|
| Agentic GRC Automation | Coordinates recurring compliance activities | Reduces administrative workload |
| AI Security Questionnaires | Generates draft responses using existing documentation | Accelerates customer security assessments |
| Automated Control Testing | Evaluates connected security controls | Identifies potential compliance gaps |
| Intelligent Risk Management | Supports risk identification and prioritization | Improves remediation planning |
| Evidence Automation | Collects and organizes supporting documentation | Reduces audit preparation effort |
| Multi-Framework Mapping | Associates common controls with multiple regulatory frameworks | Limits duplicated compliance activities |
Although these capabilities improve compliance efficiency, organizations must still independently validate AI-generated outputs and maintain appropriate human oversight.
HIPAA Security, Privacy, and Regulatory Framework Coverage
Scytale supports more than 80 security, privacy, and AI governance frameworks, allowing organizations to reuse applicable controls and evidence across different compliance programs.
This is particularly useful for healthcare software vendors serving enterprise customers that require both HIPAA safeguards and independent security assurance.
| Framework | Compliance Focus | Scytale Application |
|---|---|---|
| HIPAA | Protection of health information | Risk assessments, policies, evidence, and control monitoring |
| SOC 2 | Security and trust services controls | Audit preparation and evidence management |
| ISO 27001 | Information security management | Control mapping and certification readiness |
| ISO 42001 | Artificial intelligence management systems | AI governance workflows |
| GDPR | Personal data protection | Privacy governance and compliance documentation |
| PCI DSS | Payment card security | Security control management |
| NIST 800-53 | Information system security controls | Control assessments and documentation |
| CMMC | Defense contractor cybersecurity | Compliance readiness and evidence tracking |
Importantly, HIPAA does not provide an official government-issued compliance certification. Using Scytale does not automatically establish HIPAA compliance or replace an organization’s legal, administrative, physical, and technical safeguard obligations.
Integrations and Technical Infrastructure
Scytale provides more than 150 integrations across cloud infrastructure, identity platforms, security applications, development environments, and enterprise systems.
Its integration capabilities help organizations collect evidence directly from existing technology environments rather than relying exclusively on manual document uploads.
| Integration Category | Examples | Compliance Application |
|---|---|---|
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Cloud security configuration monitoring |
| Identity Management | Enterprise identity and access platforms | Authentication and user access reviews |
| Development Tools | GitHub and development pipelines | Change management and security evidence |
| Security Systems | Vulnerability and threat monitoring tools | Security risk identification |
| HR Systems | Employee lifecycle management platforms | Onboarding and offboarding controls |
| Workflow Management | Jira and related systems | Remediation tracking |
| Enterprise Applications | Connected business software | Automated compliance evidence collection |
Organizations processing PHI should verify integration permissions, data access boundaries, encryption, retention practices, and business associate agreement requirements before connecting sensitive systems.
Scytale Pricing and Implementation Costs in 2026
Scytale uses subscription-based pricing, with costs influenced by organizational requirements, the number of compliance frameworks, integrations, and professional services.
Public product information confirms customized subscription packages, but a universally applicable HIPAA-specific price list is not established.
| Cost Component | Pricing Structure |
|---|---|
| Core GRC Platform | Subscription-based; quotation recommended |
| HIPAA Compliance Management | Depends on selected package and scope |
| Additional Frameworks | Subject to commercial agreement |
| Dedicated GRC Advisory | Availability and scope depend on package |
| Penetration Testing | Separately scoped or bundled |
| Independent Audit Services | Subject to third-party engagement |
| Enterprise Implementation | Depends on integration and compliance complexity |
Implementation timelines vary according to organizational readiness, existing security controls, and the complexity of connected systems. A healthcare startup with established security policies may onboard faster than an enterprise managing multiple business units and legacy applications.
Organizations should request an itemized quotation covering onboarding, advisory support, integrations, annual renewal terms, and any additional assessment costs.
Customer Reviews, Strengths, and Limitations
Scytale has established a positive reputation among organizations seeking to reduce manual compliance work while retaining access to experienced GRC professionals.
An October 2026 AWS Marketplace review listing reports an aggregate rating of approximately 4.7 out of 5 from 776 ratings, including externally sourced reviews. Ratings may change over time.
Customer feedback frequently highlights centralized compliance management, automated evidence collection, and responsive advisory support. Some reviewers also identify limitations involving AI evidence evaluation, platform learning curves, and configurations that do not align with common cloud infrastructure patterns.
| Evaluation Area | Assessment |
|---|---|
| Compliance Automation | Strong automated evidence collection and continuous monitoring |
| HIPAA Functionality | Dedicated HIPAA assessments, policies, and monitoring |
| Multi-Framework Management | Extensive coverage across security and privacy frameworks |
| Human Advisory Support | Dedicated compliance specialists available |
| Cloud Integrations | Broad support for modern enterprise environments |
| Ease of Implementation | Depends on technology stack and organizational readiness |
| Pricing Transparency | Limited standardized public pricing |
| AI Reliability | Human review remains necessary |
| Healthcare Specialization | Strong compliance capabilities, but not a complete healthcare operations platform |
Best Use Cases for Scytale
Scytale is particularly suitable for healthcare technology businesses, SaaS vendors, medical software developers, and growing organizations that must manage HIPAA alongside other security and privacy obligations.
Its combination of continuous monitoring, compliance automation, and specialist advisory support makes it especially relevant for organizations with limited internal GRC resources.
However, healthcare providers seeking dedicated clinical privacy incident management, electronic health record administration, or patient consent management may require complementary software.
Overall Assessment
Scytale is a competitive HIPAA compliance software option in 2026 for organizations prioritizing AI-driven automation, continuous security monitoring, and multi-framework governance.
Its principal advantage is the combination of automated compliance workflows and access to human GRC expertise, which can help organizations reduce administrative effort and improve audit preparedness.
For healthcare technology companies managing HIPAA alongside SOC 2, ISO 27001, and other regulatory requirements, Scytale offers a scalable compliance management environment. Its suitability ultimately depends on the organization’s technology infrastructure, regulatory scope, budget, and ability to maintain effective security practices beyond the software itself.
2. Drata
Drata is an enterprise-focused security and compliance automation platform designed to help healthcare organizations, digital health companies, SaaS providers, and technology enterprises manage HIPAA requirements alongside multiple cybersecurity and privacy frameworks. Its centralized governance, risk, and compliance capabilities combine automated evidence collection, continuous control monitoring, risk management, and audit preparation.
Unlike traditional HIPAA compliance management solutions that rely primarily on manual assessments and periodic documentation reviews, Drata integrates with cloud infrastructure, identity management systems, employee devices, and enterprise applications to continuously evaluate security controls.
For organizations managing electronic protected health information (ePHI), Drata can help strengthen oversight of access controls, device security, workforce compliance, vendor risks, and security configurations. However, the platform does not independently guarantee HIPAA compliance or replace an organization’s legal and operational responsibilities.
Core HIPAA Compliance Features and Capabilities
Drata provides a centralized compliance management environment that helps organizations organize HIPAA security requirements, automate evidence collection, and identify weaknesses in their existing security controls.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| Continuous Control Monitoring | Automatically evaluates connected security controls | Identifies potential compliance weaknesses |
| Automated Evidence Collection | Collects audit evidence from integrated systems | Reduces manual documentation |
| HIPAA Compliance Framework | Organizes controls against applicable HIPAA requirements | Supports structured compliance management |
| Security Risk Assessments | Documents and evaluates cybersecurity risks | Supports HIPAA Security Rule risk analysis |
| Employee Device Monitoring | Evaluates encryption, screen locks, and endpoint configurations | Strengthens endpoint security oversight |
| Identity and Access Management | Monitors authentication and access-related controls | Supports access governance |
| Policy Management | Centralizes security policies and employee acknowledgments | Improves compliance documentation |
| Vendor Risk Management | Tracks third-party security assessments | Supports business associate risk oversight |
| Audit Readiness Dashboard | Consolidates evidence, control status, and remediation tasks | Improves audit preparation |
| Trust Center | Shares approved security and compliance information | Simplifies enterprise customer due diligence |
AI Features and Intelligent Compliance Automation
Drata incorporates artificial intelligence into compliance workflows to reduce repetitive administrative tasks, improve evidence management, and accelerate security assessments.
Its AI-enabled capabilities support compliance evidence analysis, security questionnaire responses, risk management, and trust assurance workflows.
Drata also provides AI governance functionality intended to help organizations establish visibility and oversight over artificial intelligence systems and agents operating within their environments.
For healthcare organizations, these capabilities can support AI-related security governance, although detecting AI agents does not by itself establish whether protected health information has been exposed.
| AI Capability | Primary Application | Operational Value |
|---|---|---|
| AI-Assisted Evidence Management | Supports evidence review and compliance documentation | Reduces repetitive compliance work |
| Intelligent Questionnaire Responses | Drafts answers using approved security information | Accelerates customer assessments |
| AI Governance | Supports oversight of AI systems and agents | Improves AI-related risk visibility |
| Automated Risk Workflows | Assists with risk documentation and remediation | Improves risk management efficiency |
| Continuous Compliance Monitoring | Evaluates connected security configurations | Detects control failures earlier |
| Trust Center Automation | Supports controlled sharing of security documentation | Reduces repetitive buyer inquiries |
| Cross-Framework Control Mapping | Reuses applicable controls across standards | Minimizes duplicate compliance efforts |
AI-generated evidence interpretations and questionnaire responses should undergo appropriate human validation, particularly when they concern HIPAA obligations, patient information, or contractual security commitments.
HIPAA Security and Multi-Framework Compliance Coverage
Drata supports HIPAA alongside major cybersecurity, privacy, and AI governance standards. Its cross-framework mapping capabilities enable organizations to reuse relevant security controls and evidence across multiple compliance programs.
This is particularly valuable for healthcare technology companies that must demonstrate HIPAA safeguards while pursuing SOC 2 certification or ISO 27001 accreditation.
| Compliance Framework | Primary Focus | Business Application |
|---|---|---|
| HIPAA | Healthcare information privacy and security | Protecting electronic health information |
| SOC 2 Type I and II | Security and operational control assurance | Enterprise customer trust |
| ISO 27001 | Information security management systems | International security certification |
| PCI DSS | Payment card data security | Securing payment processing environments |
| GDPR | Personal data protection | European privacy compliance |
| ISO 42001 | Artificial intelligence management | AI governance and accountability |
| DORA | Digital operational resilience | Financial technology compliance |
| NIS2 | Cybersecurity risk management | European cybersecurity obligations |
| NIST 800-53 | Security and privacy controls | Government and enterprise security programs |
| CMMC | Defense contractor cybersecurity | Defense supply chain requirements |
Drata’s cross-framework functionality can reduce duplicated evidence collection, although each framework maintains distinct requirements, assessment methods, and legal obligations.
Technical Safeguards and Enterprise Integrations
Drata integrates with hundreds of enterprise applications and infrastructure systems, including cloud services, identity providers, endpoint management platforms, security tools, and software development environments.
Its continuous compliance documentation describes more than 300 integrations and daily automated control testing, with alerts for security configuration drift. The exact integration catalog and testing frequency can vary by connector and control.
| Integration Category | Example Technologies | Security and Compliance Purpose |
|---|---|---|
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Cloud configuration monitoring |
| Identity Management | Okta, Microsoft Entra ID | Authentication and access control verification |
| Device Management | Jamf and mobile device management systems | Endpoint security monitoring |
| Development Platforms | GitHub and GitLab | Code repository and change management oversight |
| Security Monitoring | Vulnerability scanning and endpoint security tools | Security risk detection |
| HR Systems | Employee management applications | Workforce compliance tracking |
| Workflow Automation | Jira and Slack | Remediation notifications and task coordination |
| Trust Management | SafeBase Trust Center | Customer security assurance |
| Vendor Management | Third-party assessment systems | Supplier security oversight |
Endpoint monitoring can help verify device encryption, screen-lock policies, and other workstation security requirements. Organizations should confirm the coverage of each endpoint integration before relying on automated tests as compliance evidence.
Trust Center and Enterprise Security Assurance
Drata expanded its trust management capabilities through its approximately $250 million acquisition of SafeBase in February 2025.
The integration brings automated security questionnaires, centralized trust documentation, and controlled customer access to security information into Drata’s broader assurance offering.
| Trust Management Feature | Functionality | Business Benefit |
|---|---|---|
| Trust Center | Publishes approved security and compliance information | Improves transparency |
| AI Questionnaire Assistance | Drafts security assessment responses | Reduces sales-related compliance workload |
| Document Access Controls | Restricts access to sensitive assurance documents | Protects confidential information |
| NDA Workflows | Supports confidentiality requirements before document access | Strengthens information governance |
| Security Documentation Library | Centralizes policies, certifications, and reports | Accelerates due diligence |
| Customer Assurance Workflows | Supports enterprise buyer security reviews | Improves procurement efficiency |
For healthcare SaaS companies, these capabilities can help accelerate enterprise procurement processes involving hospitals, insurers, and other organizations that require detailed vendor security assessments.
Drata Pricing and Subscription Plans in 2026
Drata offers Foundation, Advanced, and Enterprise packages, with subscription costs determined through customized quotations rather than a universally published price list.
Its Foundation package supports organizations with up to 50 full-time employees and includes one eligible pre-mapped compliance framework, including HIPAA.
| Pricing Component | Foundation | Advanced | Enterprise |
|---|---|---|---|
| Target Organization | Smaller organizations, up to 50 employees | Growing and mid-market organizations | Large enterprises |
| Published Subscription Price | Custom quotation | Custom quotation | Custom quotation |
| Compliance Frameworks | One eligible framework included | Broader framework selection | Broad enterprise coverage |
| Automated Evidence Collection | Included | Included | Included |
| Continuous Monitoring | Included | Included | Included |
| Risk Management | Standard capabilities | Expanded options | Advanced capabilities |
| Custom Integrations and Tests | Limited compared with higher tiers | Supported | Supported |
| User Access Reviews | Optional add-on | Optional add-on | Included |
| Trust Center | Standard offering | Package-dependent | Package-dependent |
| Advanced Governance | Limited | Expanded | Comprehensive |
Independent market estimates sometimes place annual Drata subscriptions in the five-figure range, with enterprise deployments costing substantially more. However, specific employee-based price bands, add-on charges, and annual renewal increases cannot be treated as verified standard pricing.
Implementation and Audit Readiness Timeline
Drata implementation involves connecting infrastructure, configuring compliance frameworks, assigning control ownership, and validating collected evidence.
| Implementation Phase | Key Activities | Expected Outcome |
|---|---|---|
| Initial Configuration | Organization setup and framework selection | Compliance workspace established |
| System Integration | Connect cloud, identity, and endpoint systems | Automated evidence collection enabled |
| Control Mapping | Assign control owners and review requirements | Compliance responsibilities defined |
| Risk Assessment | Identify and document security risks | Initial risk register developed |
| Remediation | Address control failures and missing evidence | Improved security readiness |
| Audit Preparation | Review evidence and coordinate with auditors | More organized assessment process |
Smaller organizations with mature security practices may complete initial platform configuration within several weeks. Full audit readiness depends on existing controls, unresolved security gaps, audit scope, and external assessment requirements.
Customer Reviews, Strengths, and Limitations
Drata has a strong reputation among security and compliance teams for its automation capabilities, integration ecosystem, and centralized compliance workflows.
As of October 2026, G2 reports approximately 4.7 out of 5 stars from nearly 1,400 reviews. Positive feedback highlights evidence automation, compliance visibility, and usability, while some reviewers report limitations involving integration flexibility, onboarding depth, and customer support consistency.
| Evaluation Area | Assessment |
|---|---|
| Compliance Automation | Strong automated evidence collection and control testing |
| HIPAA Compliance Support | Suitable for structured HIPAA security programs |
| Multi-Framework Management | Extensive framework coverage |
| AI Governance | Emerging enterprise functionality with limited availability for certain features |
| Enterprise Integrations | Broad cloud, security, and identity ecosystem |
| Trust Management | Strong capabilities following SafeBase acquisition |
| Developer Flexibility | API access and custom testing capabilities |
| Pricing Transparency | Limited public subscription pricing |
| Implementation Complexity | Increases with infrastructure and organizational scale |
| Customer Support | Generally positive, with some inconsistent experiences reported |
| Healthcare Specialization | Strong security compliance platform rather than a dedicated clinical privacy system |
Best Use Cases for Drata
Drata is particularly well suited to healthcare technology organizations that require continuous compliance visibility across complex cloud environments.
| Organization Type | Primary Compliance Requirement | Drata Suitability |
|---|---|---|
| Healthcare SaaS Companies | HIPAA and SOC 2 | Excellent |
| Digital Health Startups | HIPAA readiness and scalable security controls | Strong |
| Health Technology Enterprises | Multi-framework compliance and governance | Excellent |
| Medical Software Developers | Secure development and access management | Strong |
| Healthcare AI Companies | AI governance and security assurance | Strong, subject to feature availability |
| Healthcare Data Processors | Risk management and security monitoring | Strong |
| Hospitals and Clinics | HIPAA privacy, security, and clinical workflows | Moderate; complementary tools may be required |
| Healthcare Vendors | Enterprise security questionnaires and trust assurance | Excellent |
Overall Assessment
Drata ranks among the leading enterprise compliance automation platforms for healthcare technology organizations in 2026, particularly those requiring continuous security monitoring, automated audit evidence, and coordinated management of multiple regulatory frameworks.
Its principal strengths include extensive integrations, customizable compliance workflows, AI-assisted governance, and enterprise trust management capabilities.
However, organizations should evaluate total subscription costs, implementation requirements, integration coverage, and the availability of specialized HIPAA privacy management features before adoption.
For growing healthcare SaaS companies and enterprises operating across multiple cloud environments, Drata represents a strong option for reducing manual compliance workloads and improving year-round security and audit readiness.
3. Vanta
Vanta is a leading trust management and compliance automation platform designed to help healthcare organizations, digital health companies, SaaS providers, and technology enterprises simplify HIPAA compliance while maintaining continuous visibility into their security environments.
The platform combines automated evidence collection, security control monitoring, risk assessments, policy management, and artificial intelligence to reduce the administrative burden associated with regulatory compliance. Vanta also supports widely recognized security frameworks, including SOC 2, ISO 27001, and GDPR, making it particularly relevant for organizations managing multiple compliance obligations.
Unlike traditional compliance solutions that depend heavily on manual documentation and periodic security assessments, Vanta connects directly to cloud infrastructure, identity management systems, employee devices, and enterprise applications to continuously evaluate security controls and identify potential compliance gaps.
Core HIPAA Compliance Features and Capabilities
Vanta provides a centralized environment for organizing HIPAA security requirements, managing compliance evidence, and monitoring the effectiveness of technical and administrative safeguards.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Compliance Management | Organizes applicable HIPAA controls and requirements | Supports structured compliance programs |
| Automated Evidence Collection | Collects security evidence from connected systems | Reduces manual audit preparation |
| Continuous Security Monitoring | Evaluates security configurations and control effectiveness | Identifies potential security weaknesses |
| Risk Assessment Management | Documents and tracks information security risks | Supports HIPAA Security Rule risk analysis |
| Employee Access Monitoring | Reviews access permissions and identity configurations | Strengthens access governance |
| Endpoint Security Monitoring | Evaluates device encryption and security settings | Supports protection of healthcare information |
| Policy Management | Centralizes policies, acknowledgments, and documentation | Improves administrative oversight |
| Vendor Risk Management | Supports third-party security assessments | Strengthens business associate oversight |
| Compliance Dashboards | Displays control status and remediation activities | Improves compliance visibility |
| Trust Center | Shares approved security and compliance documentation | Accelerates enterprise customer assessments |
Vanta can help organizations manage the security safeguards surrounding electronic protected health information (ePHI). However, the software does not independently establish HIPAA compliance or replace the need for appropriate privacy procedures, workforce training, contractual safeguards, and incident response processes.
AI Features and Intelligent Compliance Automation
Vanta incorporates AI-powered capabilities to automate repetitive governance, risk, and compliance activities. Its AI functionality supports policy creation, security questionnaire completion, vendor assessments, and compliance workflow management.
The platform uses information from connected systems and existing compliance documentation to help security teams identify missing evidence, investigate control failures, and prioritize remediation activities.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| AI-Assisted Policy Drafting | Generates draft security policies and compliance documentation | Reduces administrative effort |
| Intelligent Questionnaire Responses | Prepares answers using approved security information | Accelerates customer due diligence |
| AI Vendor Risk Assessment | Assists with evaluating third-party security risks | Improves supplier oversight |
| Compliance Evidence Analysis | Supports review and organization of security evidence | Reduces repetitive compliance tasks |
| Automated Control Monitoring | Identifies failed security tests and configuration changes | Improves risk visibility |
| AI-Assisted Remediation Guidance | Helps teams understand and prioritize compliance gaps | Supports faster corrective action |
| Cross-Framework Mapping | Reuses applicable controls across security frameworks | Minimizes duplicate compliance work |
| Natural Language Assistance | Helps users interact with compliance information | Improves accessibility for nontechnical teams |
AI-generated documentation and compliance recommendations should be reviewed by qualified personnel, particularly when addressing healthcare privacy obligations and sensitive patient information.
HIPAA Security, Privacy, and Regulatory Framework Coverage
Vanta supports HIPAA compliance alongside major information security, privacy, and governance frameworks. Its cross-framework mapping capabilities allow organizations to reuse applicable controls and evidence across multiple regulatory programs.
In 2026, Vanta also expanded its HIPAA offering with a Privacy Rule framework variant for covered entities, complementing its existing support for business associates.
| Compliance Framework | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA Security Rule | Administrative, physical, and technical safeguards | Protecting electronic health information |
| HIPAA Privacy Rule | Permitted uses and disclosures of protected health information | Privacy governance for covered entities |
| HIPAA Breach Notification Rule | Breach response and notification obligations | Supporting incident response readiness |
| SOC 2 | Security and trust services controls | Enterprise customer assurance |
| ISO 27001 | Information security management | International security certification |
| GDPR | Personal data protection | Privacy management for European operations |
| ISO 42001 | Artificial intelligence management systems | AI governance |
| PCI DSS | Payment card data security | Healthcare payment processing |
| NIST Cybersecurity Framework | Cybersecurity risk management | Enterprise security governance |
HIPAA does not have an official government-issued compliance certification. Vanta helps organizations manage relevant requirements but cannot guarantee compliance or eliminate the need for legal and operational oversight.
Technical Safeguards and Enterprise Integrations
Vanta supports more than 400 integrations across cloud infrastructure, identity providers, employee management platforms, security applications, and development tools.
Its automated monitoring engine performs recurring security tests, including hourly checks where supported, to identify control failures and configuration changes. Actual testing coverage depends on the connected systems and configured controls.
| Integration Category | Example Technologies | Compliance Application |
|---|---|---|
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Cloud security configuration monitoring |
| Identity Management | Okta and enterprise identity providers | Authentication and access control |
| Development Platforms | GitHub and version control systems | Secure development oversight |
| Device Management | Endpoint and mobile device management tools | Device encryption and security verification |
| HR Systems | Human resource information systems | Workforce lifecycle compliance |
| Security Tools | Vulnerability scanners and endpoint protection | Security risk monitoring |
| Workflow Management | Jira and task management systems | Remediation tracking |
| Employee Training | Security awareness training platforms | Workforce compliance documentation |
Multi-Entity Compliance Management
Vanta offers centralized management capabilities for organizations operating multiple subsidiaries, business units, or technology environments.
Its workspace and organizational management functionality can help healthcare groups separate compliance responsibilities while maintaining consolidated oversight.
| Capability | Business Application | Operational Benefit |
|---|---|---|
| Centralized Compliance Oversight | Monitor multiple organizational environments | Improves management visibility |
| Workspace Segmentation | Separate controls by business unit or environment | Supports clearer compliance boundaries |
| Asset Scoping | Identify systems handling protected health information | Reduces unnecessary assessment work |
| Shared Compliance Evidence | Reuse relevant documentation across programs | Improves efficiency |
| Role-Based Permissions | Assign access according to responsibilities | Strengthens governance |
| Consolidated Reporting | Review compliance activities across teams | Simplifies management reporting |
Vanta Pricing and Subscription Plans in 2026
Vanta uses customized subscription pricing influenced by employee headcount, selected compliance frameworks, platform capabilities, and additional modules.
Its published subscription structure includes Essentials, Plus, Professional, and Enterprise packages. Standardized annual prices are not publicly guaranteed.
| Pricing Component | Essentials | Plus | Professional | Enterprise |
|---|---|---|---|---|
| Target Organization | Small businesses and startups | Growing organizations | Scaling companies | Complex enterprises |
| Annual Subscription | Custom quotation | Custom quotation | Custom quotation | Custom quotation |
| Compliance Frameworks | One included framework | Package-dependent | Expanded coverage | Enterprise coverage |
| Automated Evidence Collection | Included | Included | Included | Included |
| Continuous Monitoring | Included | Included | Included | Included |
| AI Policy Assistance | Included | Included | Included | Included |
| Questionnaire Automation | Add-on or limited | Included allowance | Expanded allowance | Enterprise configuration |
| Advanced Risk Management | Limited | Package-dependent | Included | Advanced |
| Custom Monitoring | Limited | Package-dependent | Included | Advanced |
| Multi-Workspace Management | Limited | Package-dependent | Available | Available |
Independent market estimates frequently place entry-level compliance automation subscriptions around $10,000 annually, with more complex deployments costing substantially more. However, these figures should be treated as indicative market estimates rather than verified Vanta pricing.
Implementation Timeline and Compliance Readiness
Vanta can reduce the time required to establish compliance workflows by automating evidence collection and providing predefined controls and policy templates.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Initial Setup | Configure organization and compliance framework | Compliance workspace established |
| Integration Configuration | Connect cloud, identity, and employee systems | Automated evidence collection activated |
| Policy Preparation | Customize policies and assign ownership | Compliance documentation organized |
| Security Assessment | Evaluate controls and identify deficiencies | Initial compliance gaps identified |
| Remediation | Resolve failed tests and missing evidence | Improved security readiness |
| Compliance Review | Validate evidence and prepare assessments | Stronger audit preparedness |
Technical onboarding may take several weeks, while overall HIPAA readiness depends on the organization’s existing security controls, workforce practices, risk assessments, and remediation requirements.
Customer Reviews, Strengths, and Limitations
Vanta is widely recognized for its accessible user interface, extensive integrations, and automated compliance workflows.
Customer feedback commonly highlights faster evidence collection, streamlined onboarding, and improved visibility into security controls. Reported limitations include subscription costs, feature restrictions across pricing tiers, and the need for internal teams to address identified security weaknesses.
| Evaluation Area | Assessment |
|---|---|
| Compliance Automation | Strong automated evidence collection and monitoring |
| HIPAA Compliance Support | Dedicated HIPAA workflows and control mapping |
| AI Capabilities | Extensive AI-assisted compliance functionality |
| Integration Ecosystem | Broad enterprise technology coverage |
| User Interface | Generally regarded as intuitive |
| Multi-Framework Management | Strong cross-framework evidence reuse |
| Vendor Risk Management | Available through specialized functionality |
| Pricing Transparency | Limited public pricing |
| Automated Remediation | Guidance and selected AI-assisted capabilities; not universal automatic remediation |
| Implementation | Relatively streamlined for modern cloud environments |
| Healthcare Specialization | Strong security compliance capabilities, with complementary clinical privacy tools potentially required |
Best Use Cases for Vanta
Vanta is particularly suitable for healthcare technology companies and growing organizations seeking to establish repeatable compliance processes without building large internal governance teams.
| Organization Type | Primary Requirement | Vanta Suitability |
|---|---|---|
| Digital Health Startups | HIPAA compliance readiness | Excellent |
| Healthcare SaaS Providers | HIPAA and SOC 2 management | Excellent |
| Medical Technology Companies | Security controls and risk assessments | Strong |
| Healthcare AI Developers | AI governance and security monitoring | Strong |
| Healthcare Data Processors | Data security and vendor oversight | Strong |
| Multi-Entity Healthcare Groups | Centralized compliance management | Strong |
| Hospitals and Clinics | HIPAA privacy and security administration | Moderate to strong, depending on workflow needs |
| Healthcare Technology Vendors | Customer security assurance | Excellent |
Overall Assessment
Vanta is one of the leading HIPAA compliance automation platforms in 2026 for organizations prioritizing ease of implementation, continuous monitoring, and AI-assisted compliance management.
Its major strengths include extensive integrations, automated evidence collection, adaptive compliance scoping, workforce training support, and centralized risk management.
For healthcare startups, digital health companies, and growing SaaS providers, Vanta offers a scalable approach to managing HIPAA requirements alongside SOC 2, ISO 27001, and other security standards.
Organizations should nevertheless assess subscription costs, available integrations, HIPAA Privacy Rule coverage, and internal remediation responsibilities before selecting the platform.
4. Sprinto
Sprinto is an AI-powered governance, risk, and compliance (GRC) automation platform designed for cloud-native businesses, healthcare technology startups, SaaS providers, and growing enterprises seeking to simplify HIPAA compliance management.
The platform combines continuous security monitoring, automated evidence collection, intelligent risk assessments, policy management, and AI-driven compliance workflows. Unlike traditional compliance tools that emphasize periodic audits and manual documentation, Sprinto focuses on maintaining operational compliance readiness through automated security checks and ongoing risk evaluation.
Supporting more than 200 security and regulatory frameworks and over 300 integrations, Sprinto enables healthcare organizations to manage HIPAA alongside SOC 2, ISO 27001, GDPR, PCI DSS, and emerging AI governance standards.
Core HIPAA Compliance Features and Capabilities
Sprinto provides structured HIPAA compliance workflows that help organizations identify protected health information (PHI), establish security safeguards, monitor technical controls, and maintain supporting compliance documentation.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Compliance Management | Maps relevant systems, PHI flows, risks, and safeguards | Supports structured HIPAA readiness |
| Automated Evidence Collection | Collects compliance evidence from integrated systems | Reduces manual audit preparation |
| Continuous Security Monitoring | Evaluates connected systems for security control failures | Identifies compliance weaknesses |
| Security Risk Assessments | Documents and prioritizes organizational security risks | Supports HIPAA Security Rule risk analysis |
| Policy Management | Provides customizable security policies and acknowledgment workflows | Improves administrative compliance |
| Employee Compliance | Automates onboarding, training, and policy acknowledgments | Strengthens workforce security awareness |
| Device Security Monitoring | Tracks endpoint security configurations | Supports device protection requirements |
| Vendor Risk Management | Monitors supplier documentation and security assessments | Improves third-party oversight |
| Audit Management | Organizes evidence, controls, and assessment activities | Improves audit preparedness |
| Trust Center | Shares approved security and compliance information | Simplifies enterprise customer assessments |
AI Features and Intelligent Compliance Automation
Sprinto incorporates AI capabilities to improve compliance efficiency, automate risk analysis, and support governance across increasingly complex technology environments.
Its AI-powered risk management functionality continuously recalculates inherent and residual risk using signals from connected systems, vendor relationships, and compliance activities.
The platform also provides AI governance features that help organizations identify artificial intelligence tools, maintain AI system inventories, and assess potential security and regulatory risks.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| Continuous AI Risk Assessment | Recalculates organizational risk using live security signals | Improves risk visibility |
| Shadow AI Discovery | Identifies AI tools operating within connected environments | Highlights potentially unauthorized AI usage |
| AI Systems Inventory | Maintains records of organizational AI systems | Strengthens AI governance |
| AI Risk Assessments | Evaluates risks associated with AI applications | Supports responsible AI adoption |
| AI Policy Generation | Assists with drafting security and compliance policies | Reduces documentation effort |
| Intelligent Vendor Assessments | Reviews supplier security documentation | Accelerates vendor due diligence |
| AI Evidence Gap Analysis | Identifies missing or insufficient compliance evidence | Improves audit readiness |
| AI Security Questionnaires | Generates draft answers using compliance information | Reduces customer assessment workloads |
| Automated Control Mapping | Associates controls with applicable regulatory requirements | Reduces duplicated compliance work |
For healthcare organizations, Shadow AI Discovery can help identify potentially unsanctioned AI tools that may introduce PHI exposure risks. However, detecting AI usage does not independently establish whether patient information has been transmitted, stored, or improperly disclosed.
HIPAA Security and Multi-Framework Compliance Coverage
Sprinto supports more than 200 global security, privacy, and governance standards, including automated workflows for over 25 frameworks.
Its control-mapping capabilities allow organizations to reuse relevant security evidence across multiple compliance programs while identifying requirements that need additional safeguards.
| Compliance Framework | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA | Healthcare information privacy and security | Protecting PHI and electronic health information |
| SOC 2 | Security and trust services controls | Enterprise customer assurance |
| ISO 27001 | Information security management | International security certification |
| ISO 42001 | Artificial intelligence management systems | AI governance and accountability |
| GDPR | Personal data protection | Privacy management for European operations |
| PCI DSS | Payment card security | Securing healthcare payment systems |
| NIST Cybersecurity Framework | Cybersecurity risk management | Security governance and risk assessments |
| NIST AI Risk Management Framework | AI-related risk management | Managing healthcare AI risks |
| EU AI Act | Artificial intelligence regulatory obligations | Governance of applicable AI systems |
Sprinto’s HIPAA workflows primarily support security controls, risk assessments, documentation, and operational oversight. Organizations must still evaluate their obligations under the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule.
Technical Safeguards and Enterprise Integrations
Sprinto provides more than 300 integrations across cloud infrastructure, identity management systems, development environments, employee management platforms, and enterprise security applications.
These integrations enable automated collection of security evidence and continuous monitoring of connected systems.
| Integration Category | Example Technologies | Compliance Application |
|---|---|---|
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Cloud security monitoring |
| Identity Management | Okta, Google Workspace | Authentication and access governance |
| Development Platforms | GitHub and development pipelines | Secure development monitoring |
| Endpoint Management | Device management and endpoint security platforms | Device configuration verification |
| HR Systems | Employee management applications | Workforce compliance tracking |
| Security Platforms | Vulnerability and security monitoring tools | Security risk identification |
| Workflow Systems | Enterprise task management applications | Remediation coordination |
| Vendor Management | Third-party security documentation | Supplier risk assessments |
Sprinto also offers programmable monitors, customizable workflows, API access, and organizational rule engines within higher-tier packages.
Continuous Risk Management and AI Governance
A distinguishing feature of Sprinto is its emphasis on continuous risk evaluation rather than relying exclusively on scheduled assessments.
Its risk management capabilities incorporate changing signals from organizational infrastructure, vendor relationships, and compliance controls to provide updated risk visibility.
| Risk Management Capability | Functionality | Business Value |
|---|---|---|
| Continuous Risk Scoring | Updates risk assessments using connected system signals | Improves risk prioritization |
| Inherent Risk Evaluation | Assesses risk before considering mitigating controls | Establishes baseline exposure |
| Residual Risk Evaluation | Assesses remaining risk after safeguards | Supports management decisions |
| Control-to-Risk Mapping | Associates technical safeguards with identified risks | Improves risk accountability |
| Vendor Risk Monitoring | Tracks third-party security posture | Strengthens supplier oversight |
| AI System Discovery | Identifies AI adoption across monitored environments | Improves AI governance |
| Risk Treatment Tracking | Documents corrective actions and ownership | Supports remediation accountability |
Automated risk scoring complements, rather than replaces, formal HIPAA risk analysis. Healthcare organizations must still assess the confidentiality, integrity, and availability of electronic protected health information across their full operating environments.
Sprinto Pricing and Subscription Plans in 2026
Sprinto uses customized subscription pricing based on organizational size, compliance frameworks, automation requirements, and additional governance modules.
Its current commercial structure includes Foundation and Growth plans, with optional modules for advanced risk management, AI governance, vendor management, and multi-business-unit compliance.
| Pricing Component | Foundation | Growth |
|---|---|---|
| Target Organization | Startups preparing for initial compliance assessments | Growing organizations requiring advanced automation |
| Annual Subscription | Custom quotation | Custom quotation |
| Automated Compliance Frameworks | 25+ supported out of the box | Included |
| Framework Library | 200+ digitized frameworks | Included |
| Continuous Monitoring | Included | Included |
| Automated Evidence Collection | Included | Included |
| AI Policy Assistance | Included | Included |
| Vendor Risk Management | Included | Included |
| AI Security Questionnaires | 20 annually | Included, subject to package terms |
| Custom Compliance Workflows | Standard functionality | Advanced workflows |
| Programmable Monitoring | Limited | Included |
| Custom API Access | Limited | Included |
| Dedicated Customer Success Support | Standard support | Enhanced support |
| Enterprise Risk Management | Optional | Optional |
| Advanced AI Governance | Optional | Optional |
Third-party procurement estimates sometimes place Sprinto subscriptions between approximately $5,000 and $25,000 annually, depending on scope. However, these figures are indicative rather than guaranteed vendor prices.
Organizations should obtain quotations covering framework additions, support, implementation, AI governance modules, audit services, and renewal terms.
Implementation Timeline and Compliance Readiness
Sprinto emphasizes rapid onboarding through preconfigured compliance programs, automated integrations, and guided implementation.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Initial Configuration | Select HIPAA framework and establish compliance scope | Compliance workspace created |
| Infrastructure Integration | Connect cloud, identity, and security applications | Automated evidence collection enabled |
| Policy Preparation | Customize policies and assign responsibilities | Compliance documentation established |
| Risk Assessment | Identify PHI-related risks and security gaps | Initial risk register completed |
| Control Remediation | Address failed checks and missing safeguards | Improved security readiness |
| Compliance Validation | Review evidence and outstanding requirements | Stronger assessment preparedness |
Basic technical configuration may be completed within several weeks for organizations with straightforward cloud environments. However, G2’s reported average implementation time is approximately two months, indicating that full onboarding may take longer.
Actual HIPAA readiness depends on organizational security maturity, risk remediation requirements, and the effectiveness of existing administrative, physical, and technical safeguards.
Customer Reviews, Strengths, and Limitations
Sprinto has received positive customer feedback for its automated compliance workflows, responsive implementation support, and centralized evidence management.
As of October 2026, G2 reports a rating of approximately 4.7 out of 5 from more than 1,680 reviews.
Reviewers frequently highlight its ability to reduce manual evidence collection and improve audit organization. Reported limitations include occasional navigation complexity, customization restrictions, integration gaps, and pricing concerns.
| Evaluation Area | Assessment |
|---|---|
| Compliance Automation | Strong automated evidence collection and control monitoring |
| HIPAA Compliance Support | Dedicated HIPAA readiness workflows |
| AI Risk Management | Continuous risk evaluation and AI-assisted assessments |
| AI Governance | Shadow AI discovery and AI system inventory |
| Integration Ecosystem | More than 300 integrations |
| Multi-Framework Management | Extensive global framework coverage |
| User Experience | Generally positive, with some navigation concerns |
| Implementation Support | Frequently praised by reviewers |
| Pricing Transparency | Limited standardized public pricing |
| Customization | Advanced functionality depends on subscription tier |
| Healthcare Specialization | Strong security compliance focus rather than clinical workflow management |
Best Use Cases for Sprinto
Sprinto is particularly suitable for cloud-native healthcare businesses seeking continuous compliance oversight without building extensive internal GRC operations.
| Organization Type | Primary Compliance Requirement | Sprinto Suitability |
|---|---|---|
| Healthtech Startups | Initial HIPAA compliance readiness | Excellent |
| Healthcare SaaS Providers | HIPAA and SOC 2 compliance | Excellent |
| Digital Health Platforms | Continuous security monitoring | Excellent |
| Healthcare AI Companies | AI governance and PHI-related risk oversight | Strong |
| Medical Software Developers | Secure development and compliance evidence | Strong |
| Healthcare Data Processors | Security controls and risk management | Strong |
| Growing Technology Enterprises | Multi-framework compliance automation | Excellent |
| Hospitals and Clinics | Comprehensive clinical privacy and security operations | Moderate; additional tools may be necessary |
Overall Assessment
Sprinto is a strong HIPAA compliance software option in 2026 for healthcare technology startups, cloud-native SaaS companies, and growing organizations seeking automated compliance management.
Its primary advantages include continuous risk evaluation, automated evidence collection, extensive framework coverage, AI governance capabilities, and guided compliance implementation.
Compared with traditional manual compliance approaches, Sprinto can substantially reduce recurring administrative tasks and improve visibility into security control failures.
However, organizations should evaluate integration coverage, subscription costs, AI governance functionality, and HIPAA-specific privacy requirements before adoption.
For healthcare technology companies seeking a scalable platform that combines HIPAA readiness, multi-framework compliance, and continuous risk monitoring, Sprinto offers a compelling solution.
5. Secureframe
Secureframe is an AI-powered security compliance automation platform designed for healthcare technology companies, regulated enterprises, government contractors, and organizations managing complex cybersecurity requirements. The platform combines automated evidence collection, continuous security monitoring, risk management, policy administration, and compliance advisory services to simplify HIPAA compliance and enterprise audit preparation.
Secureframe is particularly relevant for healthcare organizations that must manage HIPAA alongside SOC 2, ISO 27001, NIST 800-53, NIST 800-171, CMMC, and FedRAMP-related security requirements. Its Secureframe Federal offering provides specialized compliance capabilities for organizations operating within the United States federal contracting ecosystem.
Unlike conventional compliance software focused primarily on checklists and document storage, Secureframe integrates with enterprise infrastructure to monitor security controls, identify compliance gaps, and coordinate remediation activities.
Core HIPAA Compliance Features and Capabilities
Secureframe helps healthcare organizations establish, document, and monitor the administrative and technical safeguards required to protect electronic protected health information (ePHI).
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Compliance Management | Organizes HIPAA controls, policies, and evidence | Supports structured compliance readiness |
| Automated Evidence Collection | Collects security evidence from integrated applications | Reduces manual documentation |
| Continuous Control Monitoring | Evaluates security configurations and compliance controls | Identifies potential control failures |
| Security Risk Assessments | Documents risks, safeguards, and remediation activities | Supports HIPAA Security Rule risk analysis |
| Policy Management | Generates and maintains security policies | Improves compliance documentation |
| Workforce Compliance | Tracks employee training and policy acknowledgments | Strengthens administrative safeguards |
| Background Check Monitoring | Organizes employee screening evidence | Supports workforce security programs |
| Vendor Risk Management | Assesses third-party security documentation | Improves business associate oversight |
| Audit Management | Centralizes controls, evidence, and assessment activities | Simplifies audit preparation |
| Compliance Advisory | Provides access to compliance specialists | Supports implementation and regulatory readiness |
Secureframe supports HIPAA compliance management but does not independently certify an organization as HIPAA compliant. Healthcare organizations remain responsible for implementing appropriate privacy, security, and breach notification procedures.
AI Features and Intelligent Compliance Automation
Secureframe incorporates artificial intelligence into policy generation, evidence management, security assessments, and compliance workflows.
Its AI-assisted capabilities help organizations prepare documentation, identify missing evidence, and respond to security questionnaires more efficiently.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| AI Policy Generation | Drafts security policies using organizational information | Reduces documentation effort |
| AI-Assisted Evidence Review | Helps analyze and organize compliance evidence | Improves audit preparation |
| Intelligent Security Questionnaires | Generates draft responses from approved documentation | Accelerates customer assessments |
| Automated Control Testing | Evaluates security controls using integrated system data | Improves compliance visibility |
| Risk and Control Mapping | Associates identified risks with relevant safeguards | Strengthens remediation oversight |
| Automated Remediation Workflows | Routes compliance tasks to responsible teams | Improves corrective action tracking |
| Compliance Gap Identification | Highlights missing documentation and failed controls | Supports proactive risk management |
| Cross-Framework Mapping | Reuses applicable controls across regulatory standards | Reduces duplicated compliance work |
AI-generated policies and compliance recommendations require human validation, particularly when addressing healthcare privacy obligations, federal contracting requirements, and sensitive patient information.
HIPAA Security and Multi-Framework Compliance Coverage
Secureframe supports commercial and federal cybersecurity frameworks, making it suitable for healthcare organizations operating across regulated markets.
Its cross-framework mapping functionality allows applicable controls and evidence to be reused across compliance programs while maintaining visibility into framework-specific requirements.
| Compliance Framework | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA | Healthcare information privacy and security | Protecting PHI and ePHI |
| SOC 2 | Security and trust services assurance | Enterprise customer assessments |
| ISO 27001 | Information security management | International security certification |
| ISO 42001 | Artificial intelligence management | Healthcare AI governance |
| GDPR | Personal data protection | International healthcare data processing |
| PCI DSS | Payment card security | Healthcare payment environments |
| NIST 800-53 | Federal information security controls | Government healthcare systems |
| NIST 800-171 | Protection of controlled unclassified information | Federal healthcare contracting |
| CMMC Level 2 | Defense contractor cybersecurity | Applicable defense supply chains |
| FedRAMP | Federal cloud security authorization | Cloud services serving federal agencies |
Federal Compliance and Secureframe Defense
Secureframe Defense extends the platform’s compliance management capabilities to organizations handling controlled unclassified information (CUI) or pursuing defense-related cybersecurity requirements.
The platform provides specialized functionality for System Security Plans, Plans of Action and Milestones, Supplier Performance Risk System scoring, and managed CUI environments.
| Federal Compliance Capability | Functionality | Business Benefit |
|---|---|---|
| CMMC Compliance Management | Organizes applicable CMMC controls and evidence | Supports defense contractor readiness |
| System Security Plans | Documents security architecture and safeguards | Improves federal compliance documentation |
| Remediation Plans | Tracks deficiencies and corrective actions | Supports structured risk treatment |
| SPRS Score Tracking | Manages applicable assessment scoring | Improves compliance visibility |
| Managed CUI Enclave | Supports isolated environments for sensitive information | Strengthens CUI protection |
| FedRAMP Framework Support | Organizes federal cloud security controls | Supports authorization preparation |
| NIST Control Mapping | Associates safeguards with federal requirements | Reduces duplicated compliance activities |
HIPAA compliance alone does not establish CMMC eligibility or FedRAMP authorization. Federal contracting requirements depend on the specific contract, information classification, and applicable authorization process.
Technical Safeguards and Enterprise Integrations
Secureframe supports more than 300 active integrations across cloud infrastructure, identity management, endpoint security, development systems, and workforce applications.
These integrations enable automated evidence collection and recurring monitoring of connected security controls.
| Integration Category | Example Technologies | Compliance Application |
|---|---|---|
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Infrastructure security monitoring |
| Identity Management | Okta and enterprise identity providers | Authentication and access reviews |
| Development Platforms | GitHub and development systems | Secure development oversight |
| Endpoint Management | Device management platforms | Device encryption and security checks |
| HR Systems | Employee management applications | Workforce compliance documentation |
| Security Monitoring | Vulnerability and security assessment tools | Security risk identification |
| Workflow Management | Jira and enterprise collaboration tools | Remediation coordination |
| Vendor Management | Third-party assessment workflows | Supplier risk oversight |
Secureframe Pricing and Subscription Plans in 2026
Secureframe offers three main packages: Fundamentals, Complete, and Defense.
Its published Fundamentals package starts at $7,500 annually. Complete and Defense pricing is customized according to organizational requirements, compliance scope, and selected capabilities.
| Pricing Component | Fundamentals | Complete | Defense |
|---|---|---|---|
| Annual Subscription | Starts at $7,500 | Custom quotation | Custom quotation |
| Target Organization | Startups and growing businesses | Mid-market and scaling enterprises | Defense contractors and regulated organizations |
| Infrastructure Monitoring | Included | Included | Included |
| Automated Evidence Collection | Included | Included | Included |
| Policy Management | Included | Included | Included |
| Risk Management | Standard | Advanced | Advanced |
| Vendor Risk Management | Standard | Advanced | Advanced |
| User Access Reviews | Standard capabilities | Advanced capabilities | Advanced capabilities |
| Trust Center | Included | Advanced | Advanced |
| Security Questionnaires | Limited automation | Expanded automation | Expanded automation |
| Custom Integrations | Limited | Included | Included |
| CMMC-Specific Workflows | Not the primary focus | Not the primary focus | Included |
| Managed CUI Environments | Not included as standard | Not included as standard | Available |
Organizations should request detailed quotations for additional frameworks, professional advisory services, custom integrations, federal compliance functionality, and renewal terms.
Implementation Timeline and Compliance Readiness
Secureframe uses preconfigured compliance frameworks, automated integrations, and expert guidance to accelerate onboarding.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Initial Configuration | Select frameworks and define compliance scope | Compliance workspace established |
| Infrastructure Integration | Connect cloud, identity, and security applications | Automated evidence collection enabled |
| Policy Development | Customize policies and assign responsibilities | Compliance documentation organized |
| Risk Assessment | Identify risks and evaluate safeguards | Initial risk register established |
| Control Remediation | Resolve failed controls and missing evidence | Improved security readiness |
| Audit Preparation | Validate documentation and supporting evidence | Stronger assessment preparedness |
Basic implementation may take several weeks. More complex healthcare and federal compliance programs can require substantially longer, particularly when infrastructure changes, independent assessments, or formal authorization processes are involved.
Customer Reviews, Strengths, and Limitations
Secureframe maintains a strong customer reputation for its compliance automation, policy management, and access to experienced compliance specialists.
As of October 2026, G2 reports approximately 4.7 out of 5 stars from 840 reviews.
Customer feedback frequently highlights its integrations, documentation templates, intuitive workflows, and implementation support. Reported limitations include occasional integration issues, documentation management friction, and differences between automated evidence requirements and auditor expectations.
| Evaluation Area | Assessment |
|---|---|
| HIPAA Compliance Support | Strong compliance documentation and control management |
| Federal Framework Coverage | Extensive support for NIST, CMMC, and FedRAMP-related requirements |
| AI Capabilities | Policy assistance, risk management, and remediation support |
| Automated Evidence Collection | Strong |
| Integration Ecosystem | More than 300 integrations |
| Risk Management | Advanced capabilities available |
| Compliance Advisory | Access to experienced compliance specialists |
| Pricing Transparency | Published entry price; higher tiers require quotations |
| Implementation Complexity | Moderate to high for complex environments |
| Federal Authorization | Supports preparation but does not grant authorization |
| Healthcare Specialization | Strong security governance; specialized clinical privacy tools may be required |
Best Use Cases for Secureframe
| Organization Type | Primary Requirement | Secureframe Suitability |
|---|---|---|
| Healthcare SaaS Companies | HIPAA and SOC 2 | Excellent |
| Digital Health Startups | Initial compliance readiness | Strong |
| Medical Software Developers | Secure development and risk management | Strong |
| Healthcare AI Companies | HIPAA and AI governance | Strong |
| Federal Healthcare Contractors | NIST and applicable federal security requirements | Excellent |
| Defense Health Technology Vendors | CMMC and CUI protection | Excellent |
| Healthcare Cloud Providers | FedRAMP preparation and continuous monitoring | Strong |
| Hospitals and Clinics | Clinical privacy and security administration | Moderate; complementary tools may be needed |
| Multi-Framework Enterprises | Centralized compliance governance | Excellent |
Overall Assessment
Secureframe is a strong HIPAA compliance automation platform in 2026 for healthcare technology companies, regulated enterprises, and federal contractors managing complex security obligations.
Its main differentiators include broad federal framework coverage, automated evidence collection, AI-assisted compliance workflows, and specialist advisory support.
For healthcare organizations requiring HIPAA alongside SOC 2, ISO 27001, NIST, CMMC, or FedRAMP-related controls, Secureframe offers a scalable compliance management environment.
However, organizations should assess implementation complexity, total subscription costs, federal authorization requirements, and the need for dedicated healthcare privacy management functionality before adoption.
6. Compliancy Group
Compliancy Group is a healthcare-focused compliance management platform designed for medical practices, dental clinics, hospitals, healthcare business associates, and organizations handling protected health information (PHI). Unlike general-purpose governance, risk, and compliance (GRC) platforms, Compliancy Group specializes in healthcare regulatory requirements, workforce compliance, risk assessments, and operational compliance management.
Founded in 2005, the company provides The Guard, a centralized compliance management platform that combines HIPAA policies, employee training, security risk assessments, incident reporting, vendor oversight, and regulatory documentation.
A distinguishing feature is its combination of compliance software and human guidance through dedicated Compliance Coaches. This approach makes the platform particularly suitable for smaller healthcare organizations without full-time compliance officers or specialized cybersecurity teams.
Core HIPAA Compliance Features and Capabilities
The Guard helps healthcare organizations establish, document, and maintain compliance programs addressing HIPAA Privacy, Security, and Breach Notification requirements.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Compliance Management | Centralizes regulatory requirements and compliance activities | Improves compliance oversight |
| Security Risk Assessment | Guides organizations through security risk identification | Supports HIPAA Security Rule obligations |
| Policy Management | Provides customizable policies and documentation templates | Standardizes compliance procedures |
| Employee Training | Tracks HIPAA, OSHA, and security awareness training | Strengthens workforce compliance |
| Business Associate Management | Stores and monitors Business Associate Agreements | Improves third-party oversight |
| Incident Management | Records, investigates, and tracks reported incidents | Supports breach response procedures |
| Exclusion List Screening | Checks employees and contractors against applicable exclusion lists | Reduces regulatory and reimbursement risks |
| Compliance Coaching | Provides guidance from experienced compliance professionals | Helps organizations address compliance gaps |
| Audit Preparation | Organizes documentation and remediation records | Improves regulatory assessment readiness |
| Trust Badge | Demonstrates participation in documented compliance programs | Supports patient and business partner confidence |
AI Features and Intelligent Healthcare Compliance Assistance
Compliancy Group incorporates artificial intelligence through CORA, its regulatory compliance assistant.
CORA helps healthcare administrators and compliance professionals interpret regulatory requirements, locate relevant guidance, and navigate compliance documentation.
The assistant draws on a regulatory knowledge base covering federal and state requirements, including HIPAA, OSHA, and other healthcare compliance obligations.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| CORA AI Assistant | Answers healthcare compliance questions | Reduces regulatory research time |
| Regulatory Knowledge Retrieval | Identifies relevant federal and state requirements | Improves regulatory understanding |
| Compliance Documentation Assistance | Helps users locate policies and supporting materials | Simplifies documentation management |
| Regulatory Guidance | Provides contextual information about compliance obligations | Supports administrative decisions |
| Compliance Gap Guidance | Helps teams understand identified compliance issues | Improves remediation planning |
| Policy Reference Assistance | Supports navigation of existing compliance policies | Reduces repetitive administrative work |
CORA should be treated as a compliance support tool rather than a substitute for legal advice or professional regulatory interpretation.
Healthcare organizations remain responsible for validating AI-generated guidance against applicable laws, regulatory updates, and organizational circumstances.
Healthcare Coding and Documentation Audits
Compliancy Group also offers Audit Manager+, a specialized healthcare auditing solution for reviewing medical coding, billing documentation, and provider compliance.
The platform supports facility, professional, and dental claims auditing, with configurable audit guidelines, scoring systems, and coding checks.
| Audit Capability | Functionality | Healthcare Benefit |
|---|---|---|
| Medical Coding Audits | Reviews coding accuracy and documentation | Identifies potential billing errors |
| Facility Claims Auditing | Supports institutional billing assessments | Improves claims compliance |
| Professional Claims Auditing | Reviews physician and professional billing | Supports coding accuracy |
| Dental Claims Auditing | Evaluates dental billing documentation | Strengthens dental practice oversight |
| NCCI Edit Checks | Identifies applicable coding edit conflicts during audits | Reduces coding compliance risks |
| Custom Audit Checklists | Applies organization-specific review criteria | Standardizes audit procedures |
| Provider and Coder Reviews | Evaluates documentation and coding within the same encounter | Improves audit consistency |
| Audit Reporting | Documents findings and scoring results | Supports corrective action planning |
Audit Manager+ is distinct from the platform’s core HIPAA compliance functionality. It focuses on coding, documentation, and billing compliance rather than cloud infrastructure security monitoring.
HIPAA, OSHA, and Healthcare Regulatory Coverage
Compliancy Group supports several healthcare compliance programs, including HIPAA, OSHA, workforce safety, and selected security assurance requirements.
Its healthcare-oriented approach is particularly useful for organizations that must manage both patient information protection and workplace compliance.
| Regulatory Area | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA Privacy Rule | Permitted uses and disclosures of PHI | Patient privacy management |
| HIPAA Security Rule | Protection of electronic PHI | Security risk assessments and safeguards |
| HIPAA Breach Notification Rule | Reporting applicable PHI breaches | Incident response documentation |
| HITECH Act | Healthcare information security and enforcement | Electronic health information governance |
| OSHA | Occupational health and workplace safety | Employee safety compliance |
| Fraud, Waste, and Abuse | Healthcare program integrity | Workforce training and compliance |
| OIG Exclusion Screening | Identifying excluded individuals and entities | Healthcare workforce and vendor screening |
| SOC 2 Readiness | Security and trust services controls | Healthcare vendor assurance |
| State Healthcare Privacy Requirements | Applicable state-level privacy obligations | Regional regulatory compliance |
The platform can support activities associated with an effective healthcare compliance program, including written policies, workforce education, reporting mechanisms, monitoring, and corrective action.
However, the seven elements of an effective compliance program described in federal guidance are broader organizational responsibilities that software alone cannot fulfill.
Workforce Compliance and Exclusion Screening
Compliancy Group provides centralized workforce management capabilities that help healthcare organizations monitor employee training, policy acknowledgments, screening requirements, and regulatory documentation.
| Workforce Capability | Functionality | Operational Benefit |
|---|---|---|
| Employee Training Records | Tracks course completion and participation | Improves training accountability |
| Policy Acknowledgments | Records employee acceptance of compliance policies | Strengthens documentation |
| OIG Exclusion Screening | Checks applicable federal exclusion records | Reduces employment and reimbursement risks |
| Additional Sanction Screening | Supports screening against multiple exclusion databases | Improves workforce oversight |
| Employee Documentation | Centralizes required compliance records | Simplifies administrative reviews |
| HR System Synchronization | Supports employee roster updates | Reduces manual workforce tracking |
| Compliance Dashboards | Displays outstanding employee requirements | Improves management visibility |
Organizations should verify screening frequency, database coverage, notification settings, and escalation procedures before relying on automated exclusion monitoring.
Business Associate and Third-Party Risk Management
Healthcare organizations frequently share sensitive information with billing companies, technology vendors, consultants, and other service providers.
Compliancy Group helps manage these relationships through centralized vendor documentation and Business Associate Agreement tracking.
| Vendor Management Feature | Functionality | Business Benefit |
|---|---|---|
| Business Associate Agreement Tracking | Stores and organizes signed agreements | Improves contractual oversight |
| Vendor Records | Maintains third-party compliance documentation | Centralizes supplier information |
| Agreement Status Monitoring | Tracks documentation and agreement requirements | Reduces administrative gaps |
| Vendor Risk Documentation | Records relevant compliance information | Supports third-party due diligence |
| Compliance Evidence Library | Stores supporting records | Improves assessment readiness |
The software supports business associate oversight but does not automatically determine whether every vendor relationship requires a Business Associate Agreement.
Compliancy Group Pricing and Subscription Plans in 2026
Compliancy Group historically offered subscription packages starting at $99 per month. However, its public pricing approach changed during 2026, and current subscriptions generally require customized quotations.
The last publicly documented pricing structure included Foundation, Growth, Advanced, and Elite packages, with employee-based charges and optional modules.
| Subscription Plan | Historical Starting Price, Billed Annually | Additional Employee Charges | Primary Focus |
|---|---|---|---|
| Foundation | $99 per month | $8 per employee per month | Basic compliance policies and workforce training |
| Growth | $249 per month | $10 per employee per month | Risk assessments and broader compliance management |
| Advanced | $449 per month | $10 per employee per month | Expanded healthcare compliance capabilities |
| Elite | Custom pricing, historically from $449 per month | Package-dependent | Advanced organizational requirements |
These figures reflect historical published pricing from July 2026 and should not be interpreted as guaranteed current rates.
Additional modules, incident management functionality, professional support, and organization-specific requirements may affect the total subscription cost.
Illustrative Annual Subscription Costs
The following calculations use historical annual-billing rates and exclude optional modules, taxes, and implementation fees.
| Organization Size | Foundation | Growth | Advanced |
|---|---|---|---|
| 5 Employees | $1,668 | $3,588 | $5,988 |
| 10 Employees | $2,148 | $4,188 | $6,588 |
| 25 Employees | $3,588 | $5,988 | $8,388 |
| 50 Employees | $5,988 | $8,988 | $11,388 |
Organizations comparing subscription packages should verify whether security risk assessments, vendor management, incident reporting, and Compliance Coach access are included.
Implementation and Compliance Readiness
Compliancy Group emphasizes guided implementation through its software and Compliance Coach model.
The company advertises an average of approximately 14 days to reach deal-ready documentation status for certain healthcare technology vendor workflows. This should not be interpreted as a guaranteed timeline for complete HIPAA compliance.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Initial Setup | Establish organizational profile and compliance requirements | Compliance workspace configured |
| Risk Assessment | Identify security and privacy risks | Initial compliance gaps documented |
| Policy Development | Customize policies and procedures | Administrative documentation established |
| Workforce Training | Assign training and obtain acknowledgments | Employee compliance records created |
| Vendor Documentation | Collect and organize Business Associate Agreements | Improved vendor oversight |
| Remediation | Address identified compliance deficiencies | Stronger compliance readiness |
| Ongoing Monitoring | Review training, incidents, policies, and assessments | Continuous program maintenance |
Implementation timelines depend on practice size, staffing, existing documentation, and the complexity of identified compliance gaps.
Customer Reviews, Strengths, and Limitations
Compliancy Group has established a positive reputation among healthcare administrators seeking a practical compliance management solution with accessible professional guidance.
As of October 2026, G2 reports an overall rating of approximately 4.8 out of 5, while the company reports a 4.9 out of 5 rating on Capterra.
Customer reviews frequently praise centralized compliance tracking, employee training management, and responsive coaching. Some users report limitations involving navigation, reporting flexibility, and notification workflows.
| Evaluation Area | Assessment |
|---|---|
| Healthcare Specialization | Excellent |
| HIPAA Compliance Management | Strong |
| Workforce Training | Comprehensive |
| Security Risk Assessments | Guided healthcare-focused workflows |
| Business Associate Management | Strong documentation capabilities |
| Compliance Coaching | Major competitive advantage |
| AI Regulatory Assistance | CORA provides healthcare-focused guidance |
| Medical Coding Audits | Available through Audit Manager+ |
| Cloud Infrastructure Monitoring | Limited compared with general-purpose GRC automation platforms |
| Developer Integrations | Less extensive than cloud-native compliance tools |
| Pricing Transparency | Historical pricing available; current quotations required |
| Ease of Use | Generally favorable among healthcare administrators |
Audit Support and Compliance Assurance
Compliancy Group provides audit response assistance and documented compliance verification through its Trust Badge program.
Its earlier HIPAA Seal of Compliance has been discontinued and replaced by Trust Badges for supported compliance programs.
The company advertises a 100% audit pass rate, but this is a vendor-reported claim rather than an independently established guarantee of regulatory outcomes.
Importantly, the company’s audit response terms do not guarantee a particular result or replace legal representation.
Healthcare organizations should also recognize that the United States Department of Health and Human Services does not issue official HIPAA compliance certifications.
Best Use Cases for Compliancy Group
Compliancy Group is especially suitable for healthcare providers seeking operational compliance management rather than highly technical cloud infrastructure auditing.
| Organization Type | Primary Compliance Requirement | Suitability |
|---|---|---|
| Independent Medical Practices | HIPAA policies, training, and risk assessments | Excellent |
| Dental Clinics | HIPAA and OSHA compliance | Excellent |
| Ambulatory Care Centers | Workforce compliance and patient privacy | Excellent |
| Multi-Location Medical Groups | Centralized compliance oversight | Excellent |
| Healthcare Business Associates | HIPAA documentation and vendor assurance | Excellent |
| Medical Billing Companies | HIPAA and coding compliance | Excellent |
| Hospitals | Workforce and regulatory compliance management | Strong, depending on organizational complexity |
| Healthcare SaaS Startups | HIPAA documentation and customer assurance | Strong |
| Cloud-Native Healthtech Enterprises | Automated infrastructure security monitoring | Moderate; complementary tools may be necessary |
Overall Assessment
Compliancy Group is one of the strongest healthcare-specialized HIPAA compliance software options in 2026, particularly for medical practices, dental clinics, ambulatory care providers, and healthcare business associates.
Its primary competitive advantages include healthcare-specific compliance workflows, integrated workforce training, Business Associate Agreement management, security risk assessments, AI-powered regulatory assistance, and dedicated Compliance Coach support.
Unlike general-purpose compliance automation platforms such as Vanta, Drata, and Sprinto, Compliancy Group places greater emphasis on practical healthcare administration, regulatory documentation, and guided compliance management.
However, organizations requiring extensive cloud infrastructure monitoring, developer pipeline integrations, or automated technical security evidence collection may need additional cybersecurity or GRC software.
For healthcare providers seeking a centralized platform to manage HIPAA obligations, workforce compliance, vendor relationships, and ongoing regulatory documentation, Compliancy Group represents a compelling solution in 2026.
7. Abyde
Abyde is a cloud-based HIPAA and OSHA compliance management platform designed for independent healthcare practices, dental offices, optometry clinics, medical providers, and healthcare business associates. Its primary objective is to simplify regulatory compliance through guided security risk assessments, automated policy generation, employee training, and centralized documentation.
Unlike enterprise governance, risk, and compliance (GRC) platforms that emphasize complex IT infrastructure monitoring, Abyde focuses on making HIPAA compliance accessible to healthcare administrators and practice owners without extensive technical expertise.
The platform combines software-driven compliance automation with access to healthcare compliance specialists, helping smaller organizations establish and maintain security and privacy programs while reducing administrative workloads.
Core HIPAA Compliance Features and Capabilities
Abyde provides an integrated environment for managing HIPAA Privacy, Security, and Breach Notification requirements, alongside selected OSHA workplace safety obligations.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| Security Risk Analysis | Guides practices through customized risk assessments | Supports HIPAA Security Rule risk analysis |
| Automated Policy Generation | Creates policies based on organizational characteristics | Reduces manual documentation |
| HIPAA Workforce Training | Delivers interactive courses and assessments | Improves employee compliance awareness |
| Business Associate Management | Organizes agreements with third-party service providers | Strengthens vendor oversight |
| Compliance Scorecards | Displays assessment results and outstanding requirements | Improves compliance visibility |
| Corrective Action Guidance | Identifies weaknesses and recommended improvements | Supports risk remediation |
| Incident Documentation | Records compliance events and related activities | Supports incident response management |
| Abyde Drive | Provides centralized cloud document storage | Simplifies compliance recordkeeping |
| Electronic Signatures | Supports digital execution of agreements | Reduces administrative paperwork |
| Expert Compliance Support | Provides access to compliance specialists | Assists with regulatory questions and investigations |
Intelligent Automation and Policy Generation
Abyde uses software-driven algorithms to simplify compliance assessments, documentation, and recurring administrative activities.
Its dynamic policy generation functionality uses information from organizational profiles and security risk assessments to produce customized policies reflecting relevant federal and state requirements.
Although these capabilities provide intelligent automation, Abyde should not be confused with platforms offering autonomous AI agents, generative AI risk analysis, or continuous cloud infrastructure testing.
| Automation Capability | Primary Application | Operational Benefit |
|---|---|---|
| Guided Risk Assessment | Presents relevant questions based on practice characteristics | Simplifies risk identification |
| Dynamic Policy Generation | Creates customized compliance documentation | Reduces manual policy preparation |
| Automated Risk Scoring | Organizes identified vulnerabilities and assessment results | Improves compliance prioritization |
| Corrective Action Recommendations | Suggests actions for identified deficiencies | Supports remediation planning |
| Training Notifications | Reminds employees about outstanding training | Improves completion rates |
| Compliance Progress Reporting | Tracks training and compliance activities | Reduces administrative monitoring |
| Agreement Reminders | Identifies agreements approaching expiration | Improves vendor documentation |
| Regulatory Documentation Updates | Reflects supported changes in applicable requirements | Helps maintain current policies |
HIPAA and OSHA Regulatory Coverage
Abyde offers separate compliance solutions for HIPAA-covered entities, healthcare business associates, and OSHA-regulated healthcare workplaces.
Its approach is particularly useful for small practices that must manage patient information privacy and employee workplace safety simultaneously.
| Regulatory Area | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA Privacy Rule | Protection and permitted disclosure of PHI | Patient privacy management |
| HIPAA Security Rule | Administrative, physical, and technical safeguards | Electronic health information protection |
| HIPAA Breach Notification Rule | Reporting applicable PHI breaches | Incident response procedures |
| HITECH Act | Electronic health information security | Healthcare data governance |
| OSHA Healthcare Requirements | Workplace health and safety | Employee safety programs |
| State Privacy Requirements | Applicable state-specific privacy obligations | Localized policy documentation |
| Business Associate Agreements | Contractual safeguards for PHI handling | Third-party compliance oversight |
Abyde does not independently guarantee HIPAA compliance. Organizations remain responsible for implementing appropriate safeguards, conducting accurate risk analyses, and maintaining effective privacy and security procedures.
Security Risk Analysis and Corrective Action Management
Abyde’s Security Risk Analysis module is one of its principal capabilities. It provides guided assessments tailored to organizational characteristics, helping practices evaluate risks across administrative, physical, and technical safeguards.
The platform generates compliance scorecards and recommendations based on assessment responses.
| Risk Assessment Capability | Functionality | Business Value |
|---|---|---|
| Adaptive Questionnaires | Presents questions relevant to the organization | Reduces unnecessary assessment work |
| Administrative Safeguard Review | Evaluates policies, training, and governance | Identifies procedural weaknesses |
| Physical Safeguard Review | Examines facility and equipment protection | Supports workplace security |
| Technical Safeguard Review | Assesses applicable information security practices | Highlights technical risks |
| Compliance Scorecard | Summarizes assessment results | Improves management visibility |
| Corrective Action Guidance | Identifies recommended remediation activities | Supports risk reduction |
| Assessment Collaboration | Allows internal or external contributors to answer assigned questions | Improves assessment completeness |
| Ongoing Assessment Reminders | Prompts organizations to revisit compliance requirements | Encourages continued oversight |
Automated assessments should be supplemented by appropriate technical reviews, particularly when organizations operate electronic health record systems, remote access infrastructure, or complex networks.
Employee Training and Workforce Compliance
Abyde includes interactive workforce training designed to help healthcare employees understand HIPAA obligations and applicable workplace safety requirements.
Training modules incorporate educational videos, assessments, completion records, and automated notifications.
| Training Feature | Functionality | Operational Benefit |
|---|---|---|
| Interactive Training Modules | Delivers structured compliance education | Improves employee engagement |
| Knowledge Assessments | Evaluates understanding of training materials | Supports knowledge retention |
| Automated Reminders | Notifies employees about outstanding requirements | Reduces missed training |
| Completion Tracking | Records training progress and completion | Strengthens compliance documentation |
| Training Certificates | Maintains evidence of completed education | Supports regulatory reviews |
| Progress Reporting | Provides periodic employee training summaries | Simplifies administrator oversight |
| Self-Paced Learning | Allows employees to complete training independently | Reduces scheduling disruption |
Business Associate Agreement and Document Management
Abyde provides a centralized portal for managing Business Associate Agreements (BAAs), supporting electronic signatures, document storage, and agreement status tracking.
Its Abyde Drive functionality enables practices to retain compliance documentation within a centralized cloud environment.
| Document Management Feature | Functionality | Healthcare Benefit |
|---|---|---|
| BAA Management | Organizes agreements with business associates | Improves contractual compliance |
| Electronic Signatures | Enables digital agreement execution | Reduces paperwork |
| Agreement Status Tracking | Monitors outstanding and completed agreements | Improves vendor oversight |
| Expiration Notifications | Alerts users about upcoming agreement deadlines | Supports timely reviews |
| Abyde Drive Storage | Stores compliance documents centrally | Improves record accessibility |
| Policy Documentation | Maintains organizational policies and procedures | Supports regulatory readiness |
| Incident Records | Preserves documentation of reported compliance events | Strengthens audit trails |
Technical Safeguards and Integration Capabilities
Abyde emphasizes guided compliance administration rather than extensive API-driven infrastructure monitoring.
Its functionality is therefore more closely aligned with healthcare practice management than enterprise cloud security automation.
| Technical Capability | Abyde Support | Assessment |
|---|---|---|
| Cloud-Based Compliance Portal | Available | Strong |
| Guided Security Risk Assessments | Available | Strong |
| Automated Policy Generation | Available | Strong |
| Employee Training Management | Available | Strong |
| Electronic BAA Management | Available | Strong |
| Cloud Document Storage | Available | Strong |
| Incident Documentation | Available | Strong |
| Automated AWS Security Testing | Not a core advertised capability | Limited |
| Continuous Cloud Configuration Monitoring | Not a core advertised capability | Limited |
| Developer Pipeline Integration | Not a primary product focus | Limited |
| Enterprise Multi-Framework GRC | Narrower scope than general-purpose GRC platforms | Limited |
Abyde Pricing and Subscription Plans in 2026
Abyde offers subscription-based pricing for HIPAA compliance, OSHA compliance, business associates, and standalone security risk assessments.
Capterra lists a starting price of $115 per month. However, Abyde’s own pricing calculator varies by selected product, organization size, and billing frequency.
A recent published pricing comparison identified an annual-billing cost of approximately $1,738.80 for one location with up to 10 employees.
| Pricing Component | Published or Indicative Pricing |
|---|---|
| Capterra Starting Price | $115 per month |
| Annualized Capterra Starting Price | $1,380 per year |
| HIPAA Covered Entity Plan | Varies by practice size and billing frequency |
| Example Annual-Billing Price | Approximately $1,738.80 annually for one location with up to 10 employees |
| HIPAA Business Associate Plan | Product-specific quotation or calculator |
| OSHA Healthcare Plan | Separate subscription |
| Standalone Security Risk Analysis | Separate product |
| Annual Billing Discount | 10% compared with applicable nonannual billing |
| Compliance Expert Support | Included in eligible subscriptions |
The $115 monthly starting price and the $1,738.80 annual example represent different published pricing references and should not be treated as interchangeable quotations.
Implementation Timeline and Compliance Readiness
Abyde is designed for relatively straightforward onboarding without requiring dedicated IT personnel.
Its guided questionnaires and automated documentation workflows allow smaller practices to begin compliance activities quickly.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Account Setup | Enter practice and employee information | Compliance workspace established |
| Security Risk Analysis | Complete guided assessment | Initial risks identified |
| Policy Generation | Generate and review customized policies | Compliance documentation prepared |
| Employee Training | Assign required training modules | Workforce education initiated |
| Vendor Documentation | Upload and execute BAAs | Vendor records organized |
| Corrective Actions | Address identified compliance gaps | Improved security readiness |
| Ongoing Compliance | Review reminders, assessments, and training | Continued compliance management |
Initial setup may be completed within days for small practices. However, full HIPAA readiness depends on the organization’s existing safeguards, identified risks, training completion, and remediation requirements.
Customer Reviews, Strengths, and Limitations
Abyde holds a 5.0 out of 5 rating on Capterra as of October 2026. However, this rating is based on only one published review and therefore provides limited evidence of broader customer satisfaction.
That review highlights ease of use, responsive customer support, and perceived value for money.
| Evaluation Area | Assessment |
|---|---|
| HIPAA Compliance Management | Strong for independent healthcare practices |
| OSHA Compliance | Dedicated healthcare workplace safety solution |
| Security Risk Assessments | Guided and customizable |
| Automated Policy Generation | Strong |
| Employee Training | Interactive and centrally managed |
| Business Associate Management | Electronic agreements and reminders |
| Expert Support | Included access to compliance specialists |
| Pricing Accessibility | Competitive for small healthcare organizations |
| Enterprise Cloud Monitoring | Limited |
| Developer Integrations | Limited compared with enterprise GRC platforms |
| Customer Review Evidence | Positive but very small verified review sample |
| Implementation Complexity | Relatively low for smaller practices |
Best Use Cases for Abyde
Abyde is especially suitable for smaller healthcare organizations seeking an accessible HIPAA compliance solution without the complexity of enterprise GRC platforms.
| Organization Type | Primary Compliance Requirement | Abyde Suitability |
|---|---|---|
| Independent Medical Practices | HIPAA policies, risk assessments, and training | Excellent |
| Dental Clinics | HIPAA and OSHA compliance | Excellent |
| Optometry Practices | Patient privacy and workforce compliance | Excellent |
| Small Healthcare Clinics | Compliance documentation and training | Excellent |
| Solo Healthcare Providers | Affordable compliance administration | Excellent |
| Healthcare Business Associates | HIPAA documentation and BAAs | Strong |
| Multi-Location Medical Groups | Centralized practice compliance | Moderate to strong |
| Hospitals and Health Systems | Complex regulatory and security operations | Limited |
| Cloud-Native Healthcare SaaS Companies | Continuous infrastructure monitoring | Limited |
| Large Healthcare Enterprises | Multi-framework GRC automation | Limited |
Overall Assessment
Abyde is a compelling HIPAA compliance software option in 2026 for independent medical practices, dental clinics, optometry offices, and smaller healthcare organizations.
Its principal strengths include guided security risk assessments, automated policy generation, interactive workforce training, electronic Business Associate Agreement management, and accessible compliance support.
Compared with enterprise compliance automation platforms such as Drata, Vanta, and Secureframe, Abyde offers a simpler and more healthcare-specific approach that prioritizes administrative compliance rather than extensive technical infrastructure monitoring.
However, larger healthcare enterprises and cloud-native technology companies may require additional security monitoring, risk management, and technical compliance tools.
For smaller healthcare practices seeking an affordable, user-friendly platform to organize HIPAA and OSHA compliance activities, Abyde represents a practical choice in 2026.
8. Accountable HQ
Accountable HQ is an AI-powered HIPAA compliance management platform designed for healthcare startups, independent medical practices, behavioral health clinics, healthcare business associates, and small to mid-sized organizations handling protected health information (PHI).
The platform combines automated policy management, security risk assessments, workforce training, vendor oversight, incident response, and regulatory documentation within a centralized compliance environment. Its transparent subscription pricing and self-service onboarding make it particularly attractive to smaller healthcare organizations without dedicated compliance departments.
Unlike enterprise governance, risk, and compliance (GRC) platforms that primarily focus on continuous cloud infrastructure monitoring, Accountable HQ emphasizes practical HIPAA compliance administration, AI-assisted documentation, and accessible regulatory support.
Core HIPAA Compliance Features and Capabilities
Accountable HQ provides an integrated compliance management system covering essential administrative, technical, and organizational requirements associated with HIPAA.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Compliance Management | Centralizes policies, assessments, and compliance activities | Simplifies regulatory oversight |
| Security Risk Assessment | Guides organizations through security risk evaluations | Supports HIPAA Security Rule requirements |
| AI Policy Management | Generates and maintains organization-specific compliance policies | Reduces documentation workloads |
| Employee HIPAA Training | Delivers workforce training and tracks completion | Improves employee compliance awareness |
| Business Associate Management | Organizes and tracks Business Associate Agreements | Strengthens vendor oversight |
| Incident Response | Documents and manages potential security incidents | Supports breach investigation workflows |
| Data Inventory | Maintains records of systems and sensitive information | Improves data governance |
| PHI Data Flow Mapping | Documents how protected health information moves | Supports risk identification |
| Trust Center | Shares approved compliance information with customers | Improves business partner confidence |
| Audit Logs | Records compliance activities and supporting evidence | Strengthens accountability |
| Exclusion Screening | Screens applicable employees and vendors against federal exclusion records | Reduces healthcare regulatory risks |
| Compliance Support | Provides access to compliance specialists | Assists with audits and regulatory questions |
AI Features and Intelligent Compliance Automation
Accountable HQ incorporates an AI-powered assistant called Compliance Copilot, designed to automate repetitive compliance tasks and help organizations maintain ongoing regulatory readiness.
Unlike basic AI chatbots that provide general compliance information, Compliance Copilot can use organizational records, policies, employee information, vendor inventories, assessments, and incident histories to generate recommendations and initiate approved workflows.
The platform documents more than 90 available tools supporting compliance administration.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| AI Policy Drafting | Creates organization-specific HIPAA policies | Reduces manual policy preparation |
| AI Security Risk Assessment | Suggests assessment responses and identifies information gaps | Accelerates initial risk evaluations |
| Intelligent Vendor Research | Reviews vendor compliance information and BAA availability | Improves third-party oversight |
| Automated Remediation Planning | Generates corrective action plans from assessment findings | Supports risk reduction |
| Employee Onboarding Assistance | Helps assign training and compliance responsibilities | Simplifies workforce administration |
| AI Data Flow Mapping | Supports documentation of PHI movement | Improves data visibility |
| Incident Management Assistance | Helps document and organize potential security incidents | Strengthens response coordination |
| AI Compliance Reporting | Generates reports using current compliance records | Reduces administrative reporting |
| Security Questionnaire Assistance | Supports responses to customer compliance assessments | Accelerates business due diligence |
Compliance Copilot operates with human oversight. Sensitive actions, including breach determinations and external communications, require appropriate approval rather than unrestricted autonomous execution.
HIPAA Security, Privacy, and Regulatory Coverage
Accountable HQ focuses primarily on HIPAA compliance while offering complementary functionality for workforce training, privacy management, vendor screening, and information security.
| Regulatory Area | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA Privacy Rule | Permitted uses and disclosures of PHI | Patient privacy governance |
| HIPAA Security Rule | Administrative, physical, and technical safeguards | Electronic health information security |
| HIPAA Breach Notification Rule | Assessment and reporting of applicable breaches | Incident response management |
| HITECH Act | Electronic health information protection | Healthcare data governance |
| Business Associate Requirements | Contractual protection of PHI | Third-party vendor oversight |
| OIG Exclusion Screening | Identification of excluded individuals and entities | Healthcare workforce compliance |
| Privacy Rights Management | Data access and privacy request workflows | Applicable privacy obligations |
| Security Awareness Training | Workforce cybersecurity education | Employee security practices |
| Fraud, Waste, and Abuse Training | Healthcare program integrity | Staff regulatory awareness |
Accountable HQ helps organizations document and manage compliance requirements. However, HIPAA compliance remains an ongoing organizational responsibility rather than a status automatically achieved through software subscription.
Security Risk Assessments and Remediation Management
Accountable HQ includes guided security risk assessments designed to help healthcare organizations identify risks affecting the confidentiality, integrity, and availability of electronic protected health information.
Higher-tier subscriptions provide additional remediation planning, access control reviews, and security monitoring functionality.
| Risk Management Capability | Functionality | Business Value |
|---|---|---|
| Guided Security Risk Assessment | Evaluates organizational security practices | Identifies potential HIPAA weaknesses |
| Compliance Gap Identification | Highlights missing controls and documentation | Improves compliance visibility |
| Remediation Plans | Documents corrective actions and responsibilities | Supports structured risk reduction |
| MFA Reviews | Evaluates multifactor authentication practices | Strengthens account security |
| Access Control Reviews | Assesses user permissions and access procedures | Reduces unauthorized access risks |
| Data Inventory | Identifies systems and information assets | Improves risk assessment completeness |
| Data Flow Mapping | Documents movement of protected information | Supports security analysis |
| Compliance Reports | Summarizes assessment and remediation progress | Improves management oversight |
Workforce Training and Employee Compliance
Accountable HQ includes HIPAA and security awareness training across all subscription tiers. Its Plus and Pro packages expand workforce education into additional healthcare compliance areas.
| Training Capability | Basic HIPAA | Plus | Pro |
|---|---|---|---|
| HIPAA Training | Included | Included | Included |
| Security Awareness Training | Included | Included | Included |
| Training Completion Tracking | Included | Included | Included |
| Employee Compliance Records | Included | Included | Included |
| Fraud, Waste, and Abuse Training | Not included | Included | Included |
| Sexual Harassment Training | Not included | Included | Included |
| Bloodborne Pathogens Training | Not included | Included | Included |
| Phishing Simulations | Not included | Included | Included |
| Exclusion Screening | Not included | Included | Included |
These capabilities are especially useful for medical practices and behavioral health providers seeking to consolidate employee compliance activities within a single platform.
Vendor Management and Business Associate Agreements
Accountable HQ provides vendor management and Business Associate Agreement tracking across all subscription plans.
The Plus and Pro packages introduce additional vendor discovery capabilities that can identify applications used within connected identity environments.
| Vendor Management Feature | Functionality | Healthcare Benefit |
|---|---|---|
| Vendor Inventory | Maintains records of third-party service providers | Improves supplier visibility |
| BAA Management | Sends, tracks, and stores Business Associate Agreements | Supports HIPAA contractual requirements |
| Electronic Signatures | Facilitates digital agreement execution | Reduces paperwork |
| Vendor Compliance Research | Assists with evaluating vendor security information | Supports due diligence |
| Shadow IT Discovery | Identifies applications used by employees | Highlights potentially unapproved vendors |
| Vendor Risk Questionnaires | Collects security assessment information | Strengthens third-party oversight |
| Exclusion Screening | Checks applicable parties against federal exclusion records | Reduces regulatory exposure |
Accountable HQ Pricing and Subscription Plans in 2026
Accountable HQ publishes three subscription plans: Basic HIPAA, Plus, and Pro.
All plans include core HIPAA compliance functionality, while higher tiers provide expanded security monitoring, vendor discovery, workforce training, and professional support.
| Pricing Component | Basic HIPAA | Plus | Pro |
|---|---|---|---|
| Monthly Billing | $199/month | $299/month | $799/month |
| Annual Billing Rate | $169/month | $254/month | $679/month |
| Annual Subscription Cost | $2,028 | $3,048 | $8,148 |
| Included Employees | 15 | 15 | 20 |
| Additional Employee | $9/month | $15/month | $19/month |
| Compliance Copilot | Included | Included | Included |
| Security Risk Assessment | Included | Included | Included |
| HIPAA Training | Included | Included | Included |
| Vendor and BAA Management | Included | Included | Included |
| Trust Center | Included | Included | Included |
| Exclusion Screening | Not included | Included | Included |
| Phishing Simulations | Not included | Included | Included |
| Advanced Monitoring | Limited | Included | Included |
| Dedicated Compliance Support | Not included | Not included | Included |
| Vulnerability Scanning | Not included | Not included | Twice annually |
| Penetration Testing | Not included | Not included | Once annually |
| Priority Onboarding | Not included | Not included | Included |
Annual subscriptions provide approximately 15% savings compared with standard monthly billing.
The platform also offers a seven-day free trial, allowing organizations to evaluate its compliance workflows before committing to a paid subscription.
Illustrative Annual Subscription Costs by Organization Size
The following estimates use published annual-billing rates and assume additional employee charges are applied monthly.
| Organization Size | Basic HIPAA | Plus | Pro |
|---|---|---|---|
| 10 Employees | $2,028 | $3,048 | $8,148 |
| 15 Employees | $2,028 | $3,048 | $8,148 |
| 20 Employees | $2,568 | $3,948 | $8,148 |
| 25 Employees | $3,108 | $4,848 | $9,288 |
| 50 Employees | $5,808 | $9,348 | $14,988 |
These calculations exclude taxes, additional services, and any future subscription adjustments.
Technical Safeguards and Integration Capabilities
Accountable HQ provides administrative compliance automation and selected technical security monitoring features.
Its integration ecosystem is narrower than enterprise-focused platforms such as Drata, Vanta, and Secureframe, but its capabilities address many common operational requirements of smaller healthcare organizations.
| Technical Capability | Availability | Assessment |
|---|---|---|
| Cloud-Based Compliance Portal | Available | Strong |
| AI Compliance Assistant | Available | Strong |
| Security Risk Assessments | Available | Strong |
| PHI Data Flow Mapping | Available | Strong |
| MFA and Access Reviews | Plus and Pro | Strong for administrative oversight |
| Vendor Discovery | Plus and Pro | Useful |
| Phishing Simulations | Plus and Pro | Available |
| Data Breach Monitoring | Plus and Pro | Available |
| Vulnerability Scanning | Pro | Twice annually |
| Penetration Testing | Pro | Annually |
| Enterprise SIEM Monitoring | Not a core advertised capability | Limited |
| Continuous Cloud Infrastructure Testing | Not a primary product focus | Limited |
| Developer Pipeline Integrations | Limited compared with enterprise GRC platforms | Limited |
Implementation Timeline and Compliance Readiness
Accountable HQ emphasizes self-service implementation supported by guided compliance workflows and optional professional assistance.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Account Setup | Configure organization and employee records | Compliance workspace established |
| Security Risk Assessment | Evaluate security practices and identified risks | Initial compliance gaps documented |
| Policy Development | Generate and review organizational policies | Compliance documentation prepared |
| Workforce Training | Assign HIPAA and security awareness courses | Employee training initiated |
| Vendor Documentation | Register vendors and manage BAAs | Third-party records organized |
| Remediation Planning | Address identified compliance deficiencies | Improved security readiness |
| Ongoing Monitoring | Review incidents, assessments, and training | Continued compliance management |
Small organizations may complete initial setup within one to two weeks, depending on existing documentation and internal resources. However, this is an indicative onboarding period rather than a guaranteed HIPAA compliance timeline.
Customer Reviews, Strengths, and Limitations
Accountable HQ maintains a 4.8 out of 5 rating on Capterra based on 35 reviews as of August 2026.
Customers frequently praise its straightforward interface, centralized compliance management, employee training functionality, and accessible support.
Some reviewers identify limitations involving specialized electronic health record integrations, documentation setup requirements, and the availability of advanced features across subscription tiers.
| Evaluation Area | Assessment |
|---|---|
| HIPAA Compliance Management | Strong |
| AI Compliance Automation | Extensive administrative automation |
| Pricing Transparency | Excellent |
| Employee Training | Comprehensive core functionality |
| Vendor and BAA Management | Included across all plans |
| Security Risk Assessments | Included across all plans |
| Audit Support | Available across subscription tiers |
| Dedicated Compliance Advisor | Reserved for Pro |
| Technical Security Monitoring | Moderate |
| Enterprise Infrastructure Integrations | Limited |
| Ease of Use | Generally favorable |
| Customer Satisfaction | 4.8 out of 5 on Capterra |
| Healthcare Specialization | Strong |
Audit Protection Guarantee and Compliance Assurance
Accountable HQ includes an Audit Protection Guarantee across its subscription packages.
This service provides access to compliance specialists who can help organizations prepare documentation, respond to regulatory inquiries, and navigate audit-related processes.
| Audit Support Capability | Functionality | Business Benefit |
|---|---|---|
| Audit Protection Guarantee | Provides assistance during applicable regulatory audits | Reduces administrative uncertainty |
| Compliance Documentation | Organizes policies, assessments, and training records | Improves evidence accessibility |
| Audit Response Preparation | Helps prepare responses to regulatory inquiries | Supports structured communication |
| Compliance Specialists | Provides access to experienced support personnel | Assists with compliance questions |
| Trust Center | Shares approved compliance information | Strengthens customer assurance |
| HIPAA Badge | Displays vendor-issued compliance recognition | Supports business credibility |
The Audit Protection Guarantee should not be interpreted as insurance against regulatory penalties or a promise that an organization will pass every audit.
Similarly, the HIPAA Badge is vendor-issued recognition rather than an official certification from the United States Department of Health and Human Services.
Best Use Cases for Accountable HQ
Accountable HQ is particularly suitable for smaller healthcare organizations seeking affordable HIPAA compliance software with transparent pricing and minimal implementation complexity.
| Organization Type | Primary Compliance Requirement | Suitability |
|---|---|---|
| Healthcare Startups | HIPAA policies and initial compliance readiness | Excellent |
| Independent Medical Practices | Risk assessments, training, and documentation | Excellent |
| Behavioral Health Clinics | Patient privacy and workforce compliance | Excellent |
| Healthcare Business Associates | BAAs, policies, and security assessments | Excellent |
| Medical Billing Companies | HIPAA and workforce compliance | Excellent |
| Digital Health Startups | HIPAA documentation and customer assurance | Strong |
| Multi-Location Clinics | Centralized compliance administration | Strong |
| Small Healthcare SaaS Vendors | HIPAA compliance and Trust Center functionality | Strong |
| Hospitals and Health Systems | Complex security and privacy operations | Moderate |
| Large Cloud-Native Enterprises | Continuous technical security monitoring | Limited |
Overall Assessment
Accountable HQ is one of the more accessible HIPAA compliance software platforms in 2026 for healthcare startups, independent practices, behavioral health providers, and smaller healthcare business associates.
Its principal strengths include transparent subscription pricing, AI-powered compliance administration, integrated workforce training, security risk assessments, Business Associate Agreement management, and accessible audit support.
The inclusion of Compliance Copilot across all subscription tiers is a notable differentiator, enabling smaller organizations to automate administrative tasks that would otherwise require substantial manual effort.
Compared with enterprise GRC platforms such as Drata and Vanta, Accountable HQ prioritizes healthcare-specific compliance documentation and operational simplicity rather than extensive cloud infrastructure monitoring.
For small and growing healthcare organizations seeking a cost-effective platform to organize HIPAA compliance activities and maintain ongoing regulatory readiness, Accountable HQ represents a strong option in 2026.
9. Rhythm360
Rhythm360 is a specialized cardiac remote monitoring and clinical workflow management platform designed for cardiology practices, electrophysiology clinics, hospitals, and healthcare organizations managing data from cardiac implantable electronic devices (CIEDs).
Unlike traditional HIPAA compliance software focused on governance, risk assessments, policy documentation, and regulatory audits, Rhythm360 operates as a clinical technology platform that incorporates healthcare data security and privacy safeguards into remote patient monitoring workflows.
The platform consolidates cardiac device transmissions from multiple manufacturers, applies AI-assisted clinical triage, supports electronic health record (EHR) integration, and streamlines documentation and billing processes.
Its primary value lies in helping cardiovascular care teams manage high volumes of device-generated information while maintaining appropriate controls over sensitive patient data.
Core HIPAA and Cardiac Monitoring Features
Rhythm360 combines vendor-neutral cardiac device connectivity, AI-assisted monitoring, clinical documentation, and healthcare data management.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| Multi-Vendor Device Integration | Consolidates data from supported cardiac device manufacturers | Reduces fragmented monitoring workflows |
| AI-Assisted Alert Triage | Prioritizes incoming cardiac events | Helps reduce clinical alert fatigue |
| Remote Cardiac Monitoring | Centralizes device transmissions and patient information | Improves monitoring efficiency |
| EHR Integration | Transfers relevant monitoring information into clinical records | Reduces duplicate documentation |
| Clinical Workflow Automation | Organizes monitoring tasks and follow-up activities | Improves staff productivity |
| Billing Documentation | Supports monitoring-related coding and billing workflows | Improves revenue capture processes |
| Patient Data Management | Centralizes sensitive cardiac monitoring information | Supports controlled data handling |
| Access Management | Supports authorized clinical access to patient records | Contributes to HIPAA security safeguards |
| Monitoring Dashboards | Provides visibility into patient transmissions and clinical priorities | Supports operational oversight |
AI Features and Intelligent Cardiac Monitoring
Rhythm360 uses artificial intelligence to help clinical teams interpret large volumes of cardiac monitoring information and prioritize events requiring professional review.
Its AI-assisted workflows are intended to distinguish clinically important findings from routine transmissions, reducing the administrative burden associated with manually reviewing device-generated alerts.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| AI Alert Triage | Prioritizes incoming cardiac transmissions | Helps clinicians focus on urgent findings |
| Clinical Event Classification | Organizes monitoring events by clinical relevance | Improves review efficiency |
| Alert Prioritization | Highlights transmissions requiring attention | Supports faster clinical workflows |
| Data Consolidation | Organizes information from different device manufacturers | Reduces fragmented monitoring |
| Workflow Automation | Routes monitoring tasks to appropriate staff | Reduces repetitive administration |
| Clinical Documentation Assistance | Supports structured recording of monitoring activities | Improves documentation consistency |
AI-assisted triage should complement rather than replace clinical judgment. Healthcare providers remain responsible for validating alerts, reviewing relevant patient information, and determining appropriate medical interventions.
HIPAA Security and Healthcare Data Protection
Rhythm360 is marketed as a HIPAA-compliant platform, and its developer, RhythmScience, reports SOC 2 Type II certification.
The platform uses encryption, controlled access to patient information, and audit logging to support healthcare data protection.
| Security Capability | Functionality | HIPAA Relevance |
|---|---|---|
| Data Encryption | Protects information in transit and at rest | Supports electronic PHI protection |
| Access Restrictions | Limits patient information access to authorized personnel | Supports access control requirements |
| Audit Logging | Records clinical actions and relevant system activities | Supports audit control requirements |
| EHR Data Exchange | Transfers information between connected clinical systems | Supports secure information workflows |
| Patient Record Management | Consolidates monitoring information | Improves data governance |
| SOC 2 Type II Assurance | Independent assessment of applicable service controls | Provides additional security assurance |
| Clinical Documentation | Maintains monitoring and reporting records | Supports operational accountability |
Specific encryption algorithms, mandatory multifactor authentication configurations, and six-year retention of all technical audit logs should be confirmed directly with the vendor. These details are not sufficiently established by publicly available product documentation.
HIPAA requires covered entities and business associates to implement appropriate safeguards based on their responsibilities and risk assessments. A software vendor’s HIPAA compliance claim does not automatically establish compliance for every customer deployment.
Cardiac Device and EHR Integrations
One of Rhythm360’s principal advantages is its vendor-neutral integration architecture.
The platform consolidates information from major cardiac device manufacturers, reducing the need for clinical teams to manage separate monitoring portals.
| Device Manufacturer | Supported Monitoring Application | Clinical Benefit |
|---|---|---|
| Medtronic | Cardiac implantable device monitoring | Centralized device information |
| Abbott | Cardiac rhythm and implantable device monitoring | Unified clinical review |
| Boston Scientific | Cardiac device transmissions | Consolidated alert management |
| Biotronik | Remote cardiac device monitoring | Reduced portal fragmentation |
| MicroPort | Supported implantable cardiac devices | Broader device coverage |
Rhythm360 also supports bidirectional integration with major EHR systems through healthcare interoperability technologies, including HL7 and FHIR.
| EHR Platform | Integration Capability | Operational Benefit |
|---|---|---|
| Epic | Bidirectional clinical data integration | Reduces duplicate chart entry |
| Oracle Health Cerner | Clinical information exchange | Improves workflow continuity |
| Athenahealth | Monitoring documentation exchange | Simplifies practice workflows |
| eClinicalWorks | Clinical record integration | Supports centralized documentation |
| Greenway Health | EHR workflow connectivity | Improves monitoring coordination |
Integration availability and implementation requirements depend on the EHR environment, interface permissions, and selected services.
Remote Monitoring Billing and Revenue Optimization
Rhythm360 supports documentation and billing workflows associated with cardiac device monitoring and remote physiological monitoring.
The platform helps clinical teams track monitoring activities, generate reports, and identify eligible billing opportunities.
| Billing Capability | Functionality | Financial Benefit |
|---|---|---|
| Automated CPT Documentation | Records qualifying monitoring activities | Reduces missed documentation |
| Billing Workflow Integration | Connects clinical monitoring with billing processes | Improves operational efficiency |
| Monitoring Activity Tracking | Documents relevant transmissions and reviews | Supports billing accuracy |
| Revenue Dashboards | Displays monitoring-related financial information | Improves revenue visibility |
| EHR Synchronization | Transfers documentation into clinical systems | Reduces duplicate administration |
| Billing Compliance Support | Organizes supporting clinical records | Strengthens billing review processes |
Clinical and Financial Performance Indicators
RhythmScience publishes several performance indicators describing its cardiac monitoring operations.
| Performance Indicator | Reported Result | Interpretation |
|---|---|---|
| Patients Served | More than 1.5 million | Reported platform reach |
| Participating Clinics | More than 75 | Reported clinical adoption |
| Atrial Fibrillation Alerts | 52% reduction | Reported decrease in alert volume |
| Critical Condition Detection | 4 days faster | Reported average improvement |
| Provider Agreement With Technician Findings | 99.8% | Reported agreement within its monitoring service model |
| Average Return on Investment | 3 times | Vendor-reported financial return |
| Critical Alert Response | Up to 80% faster | Vendor-reported performance in selected workflows |
| Monitoring Revenue Improvement | Up to 300% | Vendor-reported potential improvement in selected use cases |
These figures represent vendor-reported outcomes and should not be interpreted as independently verified results applicable to every healthcare organization.
In particular, a 300% revenue increase is not equivalent to a guaranteed threefold return on investment. Actual financial results depend on patient volumes, payer policies, staffing costs, reimbursement eligibility, and billing accuracy.
Rhythm360 Pricing and Subscription Structure in 2026
Rhythm360 uses customized subscription pricing based on clinical requirements, patient monitoring volumes, EHR integrations, and selected services.
Standardized subscription prices are not publicly disclosed.
| Pricing Component | Structure |
|---|---|
| Core Platform Subscription | Custom quotation |
| Patient Monitoring Volume | Contract-dependent |
| Device Manufacturer Connections | Based on implementation requirements |
| EHR Integration | Included or scoped within commercial agreement |
| Clinical Monitoring Services | Optional service arrangements |
| Administrative Support | Depends on selected package |
| Billing Automation | Package-dependent |
| Implementation and Training | Defined during onboarding |
| Enterprise Deployment | Customized commercial agreement |
Healthcare organizations should request detailed quotations covering software licensing, implementation, clinical monitoring services, data migration, support, and ongoing operational costs.
Implementation Timeline and Clinical Onboarding
RhythmScience reports that most practices can begin using Rhythm360 within days to weeks, depending on integration complexity.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Initial Assessment | Review patient volumes, device manufacturers, and workflows | Deployment scope established |
| Device Integration | Connect supported manufacturer systems | Consolidated device data |
| EHR Configuration | Establish clinical data exchange | Integrated patient records |
| Alert Configuration | Define monitoring priorities and escalation procedures | Structured clinical triage |
| Billing Setup | Configure documentation and billing workflows | Improved billing readiness |
| Staff Training | Train clinical and administrative personnel | Operational adoption |
| Validation | Verify data accuracy, access controls, and reporting | Safer production operation |
Complex hospital environments may require additional testing, cybersecurity reviews, and integration validation before production deployment.
Customer Reviews, Strengths, and Limitations
Rhythm360 has a narrower publicly documented customer review footprint than mainstream HIPAA compliance management platforms.
A widely substantiated independent aggregate rating of 4.8 out of 5 could not be established from the reviewed public evidence. Its provider application has a 5.0 rating on the Apple App Store, but that rating is based on only one review and is not representative of broad customer satisfaction.
| Evaluation Area | Assessment |
|---|---|
| Cardiac Monitoring Specialization | Excellent |
| Multi-Vendor Device Integration | Strong |
| AI-Assisted Alert Triage | Strong |
| EHR Integration | Broad support for major EHR platforms |
| HIPAA Security Support | Healthcare-specific security safeguards |
| SOC 2 Assurance | Vendor-reported Type II certification |
| Clinical Workflow Automation | Strong |
| Billing Documentation | Specialized cardiac monitoring functionality |
| Pricing Transparency | Limited |
| Independent Customer Reviews | Limited publicly verified evidence |
| General HIPAA Policy Management | Not a primary product function |
| Enterprise GRC Automation | Limited compared with dedicated compliance platforms |
Best Use Cases for Rhythm360
| Organization Type | Primary Requirement | Rhythm360 Suitability |
|---|---|---|
| Cardiology Practices | Centralized cardiac device monitoring | Excellent |
| Electrophysiology Clinics | Arrhythmia alert triage and device management | Excellent |
| Cardiac Device Clinics | Multi-manufacturer monitoring | Excellent |
| Hospital Cardiology Departments | Integrated monitoring and EHR workflows | Strong |
| Remote Cardiac Monitoring Providers | Monitoring automation and billing documentation | Excellent |
| Heart Failure Programs | Integrated cardiac monitoring, with complementary products | Strong |
| General Medical Practices | HIPAA documentation and workforce compliance | Limited |
| Healthcare SaaS Companies | SOC 2 and HIPAA compliance automation | Limited |
| Large Enterprise GRC Teams | Multi-framework governance and risk management | Limited |
Overall Assessment
Rhythm360 is a specialized healthcare technology platform in 2026 for cardiology practices, electrophysiology clinics, and remote cardiac monitoring programs seeking to consolidate device information, improve alert management, and streamline clinical documentation.
Its major strengths include vendor-neutral cardiac device integration, AI-assisted clinical triage, bidirectional EHR connectivity, automated monitoring documentation, and healthcare-oriented security controls.
However, Rhythm360 should be classified primarily as HIPAA-compliant clinical monitoring software rather than comprehensive HIPAA compliance management software.
Unlike Drata, Vanta, Secureframe, or Compliancy Group, Rhythm360 is not primarily designed to manage enterprise-wide HIPAA risk assessments, workforce compliance programs, regulatory policies, or multi-framework audit readiness.
For cardiology organizations seeking secure and efficient cardiac monitoring operations, Rhythm360 offers substantial clinical value. For organizations seeking a standalone HIPAA compliance management platform, dedicated compliance software would be the more appropriate choice.
10. ComplyJet
ComplyJet is an AI-powered compliance automation platform designed for healthcare technology startups, SaaS developers, digital health companies, and business associates seeking an affordable way to manage HIPAA compliance alongside other information security frameworks.
The platform combines continuous security monitoring, automated evidence collection, AI-assisted policy management, risk assessments, workforce training, and audit preparation within a centralized compliance environment.
Unlike traditional enterprise governance, risk, and compliance (GRC) platforms that often charge according to employee headcount, selected frameworks, and additional modules, ComplyJet emphasizes predictable subscription pricing for smaller organizations.
With more than 350 integrations and support for major frameworks including HIPAA, SOC 2, ISO 27001, GDPR, and ISO 42001, ComplyJet is particularly relevant for healthcare software companies operating modern cloud infrastructure.
Core HIPAA Compliance Features and Capabilities
ComplyJet provides an integrated compliance management environment that helps healthcare technology organizations establish security safeguards, document regulatory requirements, and maintain evidence of ongoing compliance activities.
| Feature | Functionality | Benefits for Healthcare Organizations |
|---|---|---|
| HIPAA Compliance Management | Organizes applicable HIPAA safeguards and requirements | Supports structured compliance readiness |
| Automated Evidence Collection | Collects security evidence from connected systems | Reduces manual documentation |
| Continuous Control Monitoring | Evaluates connected security configurations | Identifies potential control failures |
| Security Risk Analysis | Documents organizational security risks | Supports HIPAA Security Rule risk analysis |
| AI Policy Management | Generates and manages security policies | Reduces compliance administration |
| Employee HIPAA Training | Tracks workforce education and acknowledgments | Strengthens administrative safeguards |
| Business Associate Management | Organizes Business Associate Agreements | Improves vendor oversight |
| Access Review Automation | Documents access permissions across connected systems | Supports access governance |
| Breach Notification Readiness | Provides incident response and notification procedures | Improves breach preparedness |
| Audit Workspace | Centralizes policies, evidence, and assessments | Simplifies compliance reviews |
| Trust Center | Shares approved security and compliance information | Supports enterprise customer assurance |
AI Features and Intelligent Compliance Automation
ComplyJet incorporates AI-powered capabilities to help organizations automate repetitive compliance activities, generate documentation, and identify security control weaknesses.
Its ComplyJet AI Agent assists with compliance workflows, while AI-generated fixes help technical teams investigate and address failed security tests.
The platform also supports AI-assisted policy drafting and integration with external AI assistants for reviewing compliance information.
| AI Capability | Primary Application | Operational Benefit |
|---|---|---|
| ComplyJet AI Agent | Assists with compliance management activities | Reduces repetitive administration |
| AI Policy Drafting | Generates customized security policies | Accelerates documentation |
| AI-Generated Remediation | Suggests fixes for failing security tests | Supports faster corrective action |
| Automated Gap Identification | Highlights missing evidence and control failures | Improves compliance visibility |
| AI Compliance Queries | Allows users to retrieve compliance information through natural language | Simplifies regulatory oversight |
| Intelligent Risk Documentation | Supports risk scoring and treatment records | Improves risk management |
| AI-Assisted Evidence Management | Organizes compliance documentation | Reduces audit preparation effort |
| Questionnaire Automation | Supports responses to customer security assessments | Accelerates vendor due diligence |
AI-generated policies and remediation recommendations should be reviewed by qualified personnel before implementation.
The platform’s AI capabilities support compliance management but do not independently establish that an organization satisfies every HIPAA requirement.
HIPAA Security, Privacy, and Regulatory Framework Coverage
ComplyJet supports HIPAA alongside several widely recognized security, privacy, and AI governance frameworks.
Its multi-framework functionality enables organizations to reuse relevant security controls and supporting evidence across different compliance programs.
| Compliance Framework | Primary Focus | Healthcare Application |
|---|---|---|
| HIPAA Privacy Rule | Protection and permitted disclosure of PHI | Patient privacy governance |
| HIPAA Security Rule | Administrative, physical, and technical safeguards | Electronic health information security |
| HIPAA Breach Notification Rule | Notification obligations following applicable breaches | Incident response readiness |
| SOC 2 | Security and trust services controls | Enterprise customer assurance |
| ISO 27001 | Information security management | International security certification |
| ISO 42001 | Artificial intelligence management systems | Healthcare AI governance |
| GDPR | Personal data protection | International healthcare data processing |
| PCI DSS | Payment card data security | Healthcare payment security |
ComplyJet’s HIPAA offering includes policy templates, technical safeguard monitoring, risk analysis workflows, workforce training, Business Associate Agreement tracking, and breach notification procedures.
HIPAA does not provide an official government-issued compliance certification. Organizations remain responsible for implementing appropriate safeguards and maintaining effective compliance programs.
Technical Safeguards and Enterprise Integrations
ComplyJet supports more than 350 integrations connecting cloud infrastructure, identity providers, development environments, employee management systems, and enterprise applications.
Its integration architecture enables automated collection of security evidence and ongoing monitoring of connected technical controls.
| Integration Category | Example Technologies | Compliance Application |
|---|---|---|
| Cloud Infrastructure | AWS, Microsoft Azure, Google Cloud | Cloud security monitoring |
| Identity Management | Okta, Microsoft Entra ID | Authentication and access reviews |
| Productivity Systems | Google Workspace, Microsoft 365 | User access and configuration monitoring |
| Development Platforms | GitHub and development tools | Secure development oversight |
| Endpoint Management | Hexnode and supported device management systems | Device security monitoring |
| HR Systems | Connected employee management applications | Workforce compliance tracking |
| Workflow Management | Supported task management integrations | Remediation coordination |
| AI Assistants | ChatGPT and Claude integrations | Compliance information retrieval and workflow assistance |
ComplyJet monitors supported technical safeguards, including access controls, encryption settings, audit logging, and system integrity controls.
However, its published integration catalog should not be interpreted as confirmation that every EHR system, patient portal, or healthcare database is directly supported.
Organizations should verify individual connector availability, permissions, and PHI handling arrangements before implementation.
Continuous Monitoring and Risk Management
ComplyJet emphasizes continuous compliance monitoring rather than relying exclusively on periodic manual assessments.
Its automated testing workflows help identify failed controls, configuration changes, and missing security evidence.
| Monitoring Capability | Functionality | Business Value |
|---|---|---|
| Continuous Control Testing | Evaluates supported security controls | Identifies security weaknesses |
| Configuration Monitoring | Detects changes in connected systems | Improves security visibility |
| Access Reviews | Documents user permissions and access responsibilities | Strengthens access governance |
| Encryption Monitoring | Evaluates supported encryption configurations | Supports electronic PHI protection |
| Audit Log Collection | Organizes compliance activity records | Improves accountability |
| Risk Register | Documents identified risks and treatment plans | Supports structured risk management |
| Failed-Test Notifications | Alerts teams about control failures | Accelerates remediation |
| Remediation Tracking | Coordinates corrective actions | Improves operational follow-through |
Continuous monitoring supports HIPAA compliance but does not replace formal risk analysis, physical safeguard assessments, workforce oversight, or incident response planning.
ComplyJet Pricing and Subscription Plans in 2026
ComplyJet offers transparent annual subscription pricing for startups with up to 50 employees.
Its dedicated HIPAA offering lists $5,000 annually for one framework and $8,000 annually for two frameworks, such as HIPAA and SOC 2.
However, its general pricing page and G2 listing display different starting prices, reflecting differences in package configuration and commercial terms.
| Pricing Component | Published Pricing | Key Details |
|---|---|---|
| HIPAA Single-Framework Package | $5,000 per year | HIPAA platform, onboarding, support, and Trust Center |
| HIPAA Two-Framework Package | $8,000 per year | HIPAA plus another supported framework |
| General Core Package | From $7,999 per year | General pricing page; package-dependent |
| G2 Core Listing | From $3,999 per year | Third-party listed starting price |
| G2 Plus Listing | From $6,499 per year | Third-party listed starting price |
| Employee Limit | Up to 50 employees | Startup pricing eligibility |
| Additional Employees | No per-seat charges within eligible startup packages | Predictable team scaling |
| Additional Frameworks | Custom pricing | Depends on selected package |
| External Audit | Included in certain general packages; separate for some HIPAA arrangements | Confirm contractual scope |
| Optional Services | Custom quotation | Penetration testing, virtual CISO, and managed services |
The different published prices should not be treated as interchangeable quotations. Prospective customers should confirm the exact HIPAA package, contract duration, framework coverage, and audit arrangements.
Illustrative HIPAA Subscription Cost by Team Size
The following table illustrates the annual cost per employee using the published $5,000 single-framework and $8,000 two-framework HIPAA packages.
| Organization Size | HIPAA Only Annual Cost | HIPAA + SOC 2 Annual Cost | HIPAA Only Cost per Employee |
|---|---|---|---|
| 5 Employees | $5,000 | $8,000 | $1,000 |
| 10 Employees | $5,000 | $8,000 | $500 |
| 20 Employees | $5,000 | $8,000 | $250 |
| 30 Employees | $5,000 | $8,000 | $166.67 |
| 40 Employees | $5,000 | $8,000 | $125 |
| 50 Employees | $5,000 | $8,000 | $100 |
These calculations assume the organization qualifies for the published startup pricing and exclude optional services and separately billed audits.
Implementation Timeline and Compliance Readiness
ComplyJet emphasizes guided onboarding, automated integrations, and dedicated implementation assistance.
Its general pricing documentation describes four to five implementation check-ins over approximately six to eight weeks.
Although initial technical setup can be completed more quickly, a universal seven-day guarantee for full HIPAA readiness is not substantiated by the published implementation details.
| Implementation Stage | Main Activities | Expected Outcome |
|---|---|---|
| Initial Configuration | Define HIPAA scope and organizational responsibilities | Compliance workspace established |
| Infrastructure Integration | Connect cloud, identity, and security systems | Automated evidence collection enabled |
| Risk Assessment | Identify risks affecting electronic PHI | Initial risk register developed |
| Policy Development | Customize HIPAA policies and procedures | Compliance documentation prepared |
| Workforce Training | Assign training and record acknowledgments | Employee compliance records established |
| Vendor Documentation | Organize Business Associate Agreements | Improved third-party oversight |
| Remediation | Address control failures and missing safeguards | Stronger compliance readiness |
| Compliance Review | Validate evidence and assessment documentation | Improved audit preparedness |
Implementation duration depends on existing security maturity, organizational complexity, available resources, and the extent of required remediation.
Customer Reviews, Strengths, and Limitations
ComplyJet holds a 4.8 out of 5 rating on G2 based on 17 reviews as of October 2026.
Reviewers frequently praise its intuitive interface, responsive onboarding support, affordable pricing, and automated compliance workflows.
However, its relatively small review sample provides less extensive independent customer evidence than established competitors such as Vanta, Drata, and Secureframe.
| Evaluation Area | Assessment |
|---|---|
| HIPAA Compliance Management | Strong startup-focused workflows |
| AI Compliance Automation | AI agent, policy drafting, and remediation assistance |
| Automated Evidence Collection | Strong |
| Continuous Security Monitoring | Supported across connected systems |
| Integration Ecosystem | More than 350 integrations |
| Multi-Framework Management | HIPAA, SOC 2, ISO 27001, and additional frameworks |
| Pricing Transparency | Strong, although package listings differ |
| Employee-Based Pricing | Flat pricing for eligible teams up to 50 employees |
| Implementation Support | Guided onboarding and dedicated assistance |
| Enterprise Brand Recognition | Smaller footprint than established market leaders |
| Customer Review Volume | Limited |
| Complex Healthcare Integrations | Require individual verification |
| Large Enterprise Suitability | Less established than enterprise-focused GRC platforms |
Best Use Cases for ComplyJet
ComplyJet is particularly suitable for smaller healthcare technology companies seeking affordable compliance automation without extensive internal GRC resources.
| Organization Type | Primary Compliance Requirement | ComplyJet Suitability |
|---|---|---|
| Healthtech Startups | Initial HIPAA readiness | Excellent |
| Healthcare SaaS Developers | HIPAA and SOC 2 management | Excellent |
| Digital Health Platforms | Cloud security and compliance evidence | Excellent |
| Healthcare Business Associates | HIPAA safeguards and BAA tracking | Excellent |
| Medical Software Startups | Security controls and audit preparation | Strong |
| Healthcare AI Companies | HIPAA and AI governance frameworks | Strong |
| Small Healthcare Technology Vendors | Customer security assurance | Excellent |
| Growing SaaS Companies | Multi-framework compliance automation | Strong |
| Independent Medical Practices | HIPAA training and documentation | Moderate |
| Hospitals and Health Systems | Complex clinical privacy and security operations | Limited to moderate |
| Large Healthcare Enterprises | Extensive enterprise governance | Less established |
Overall Assessment
ComplyJet is a competitive HIPAA compliance automation platform in 2026 for healthcare startups, SaaS developers, and small to midsize business associates seeking predictable pricing and automated security oversight.
Its principal strengths include flat-rate startup pricing, more than 350 integrations, AI-assisted compliance workflows, continuous control monitoring, guided implementation, and multi-framework support.
Compared with larger competitors such as Drata and Vanta, ComplyJet emphasizes affordability, hands-on onboarding, and straightforward compliance management for smaller technology teams.
However, organizations should verify current subscription terms, audit fees, integration compatibility, and the scope of AI automation before purchasing.
For cloud-native healthcare startups seeking to manage HIPAA alongside SOC 2 or ISO 27001 without committing to a complex enterprise GRC platform, ComplyJet represents a strong value-oriented option in 2026.
Conclusion
Selecting the best HIPAA compliance software in 2026 is an increasingly important decision for healthcare organizations, medical practices, healthtech startups, and business associates seeking to protect sensitive patient information while navigating evolving regulatory requirements. As healthcare systems become more interconnected and cyber threats grow more sophisticated, organizations must move beyond manual compliance checklists toward automated risk assessments, continuous security monitoring, workforce training, and comprehensive data protection strategies.
The top 10 HIPAA compliance software solutions in 2026 offer different capabilities tailored to organizational size, technical infrastructure, and regulatory complexity. Enterprise-focused platforms such as Drata, Vanta, Secureframe, Scytale, and Sprinto excel in automated evidence collection, multi-framework compliance management, and continuous control monitoring. Meanwhile, Compliancy Group, Abyde, and Accountable HQ provide healthcare-specific compliance workflows, making them particularly suitable for medical practices, dental clinics, and smaller healthcare organizations. ComplyJet offers an accessible alternative for cloud-native healthcare startups, while Rhythm360 specializes in HIPAA-conscious cardiac remote monitoring rather than general compliance management.
Artificial intelligence is also transforming HIPAA compliance management in 2026. AI-powered policy generation, automated security risk analysis, intelligent vendor assessments, and proactive compliance monitoring help organizations reduce administrative workloads and identify potential security gaps more efficiently. However, AI automation cannot replace human oversight, regulatory expertise, or the implementation of appropriate administrative, physical, and technical safeguards.
When comparing HIPAA compliance software, organizations should evaluate several critical factors, including HIPAA Privacy and Security Rule coverage, automated risk assessments, employee training, Business Associate Agreement management, integration compatibility, data encryption, audit logging, implementation complexity, and total subscription costs. Healthcare technology companies may benefit from platforms supporting SOC 2 and ISO 27001 alongside HIPAA, while independent medical practices may prioritize affordability, ease of use, and dedicated compliance guidance.
Ultimately, the best HIPAA compliance software is the solution that aligns with an organization’s operational requirements, security maturity, regulatory responsibilities, and long-term growth objectives. Investing in the right platform can streamline compliance administration, strengthen patient data protection, improve audit readiness, and build trust with patients, healthcare partners, and enterprise customers.
As healthcare digital transformation accelerates, organizations that adopt scalable, well-integrated HIPAA compliance management solutions will be better positioned to maintain regulatory readiness, respond to emerging cybersecurity risks, and protect electronic protected health information throughout 2026 and beyond.
If you find this article useful, why not share it with your hiring manager and C-level suite friends and also leave a nice comment below?
We, at the 9cv9 Research Team, strive to bring the latest and most meaningful data, guides, and statistics to your doorstep.
To get access to top-quality guides, click over to 9cv9 Blog.
To hire top talents using our modern AI-powered recruitment agency, find out more at 9cv9 Modern AI-Powered Recruitment Agency.
People Also Ask
What is the best HIPAA compliance software in 2026?
The best HIPAA compliance software in 2026 includes Scytale, Drata, Vanta, Sprinto, Secureframe, Compliancy Group, Abyde, Accountable HQ, and ComplyJet. The ideal choice depends on organizational size, security requirements, budget, and compliance needs.
What is HIPAA compliance software?
HIPAA compliance software helps healthcare organizations and business associates manage regulatory obligations, conduct security risk assessments, protect patient information, track compliance activities, and maintain documentation required under HIPAA.
Why is HIPAA compliance software important for healthcare organizations?
HIPAA compliance software helps healthcare organizations identify security vulnerabilities, safeguard patient information, manage regulatory requirements, and prepare for audits. It also reduces administrative workloads through automated compliance processes.
How much does HIPAA compliance software cost in 2026?
HIPAA compliance software pricing varies by vendor, organization size, features, and service level. Some providers offer affordable monthly subscriptions, while enterprise platforms require custom annual contracts and implementation fees.
Which HIPAA compliance software is best for small medical practices?
Compliancy Group, Abyde, and Accountable HQ are options for small medical practices. Their healthcare-focused compliance workflows can help smaller organizations manage risk assessments, staff training, documentation, and regulatory responsibilities.
What is the best HIPAA compliance software for healthcare startups?
Healthcare startups can evaluate Vanta, Drata, Secureframe, Sprinto, Scytale, and ComplyJet. These platforms offer varying levels of compliance automation, security monitoring, and support for additional frameworks such as SOC 2 and ISO 27001.
Can HIPAA compliance software guarantee HIPAA compliance?
No. HIPAA compliance software cannot guarantee regulatory compliance. Organizations remain responsible for implementing appropriate safeguards, maintaining policies, training employees, managing business associates, and meeting applicable HIPAA requirements.
What features should the best HIPAA compliance software include?
Important features include security risk assessments, compliance dashboards, policy management, workforce training, audit documentation, vendor management, incident tracking, access monitoring, and automated evidence collection.
Does HIPAA compliance software use artificial intelligence?
Some HIPAA compliance platforms use artificial intelligence to assist with policy drafting, evidence reviews, risk identification, and compliance workflows. AI capabilities vary by provider and still require human verification and oversight.
What is the difference between HIPAA compliance software and healthcare cybersecurity software?
HIPAA compliance software focuses on regulatory workflows, risk assessments, policies, and documentation. Healthcare cybersecurity software primarily protects systems and information through security controls, threat detection, and incident prevention.
Which HIPAA compliance software supports SOC 2 and ISO 27001?
Drata, Vanta, Secureframe, Sprinto, and Scytale support multiple compliance frameworks, including SOC 2 and ISO 27001. Organizations should verify the exact frameworks, integrations, and services available in their selected plans.
Is HIPAA compliance software required by law?
HIPAA does not require organizations to purchase specific compliance software. However, covered entities and business associates must satisfy applicable HIPAA requirements, including risk analysis, safeguards, documentation, and workforce training.
How does HIPAA compliance software help with security risk assessments?
HIPAA compliance software helps organizations identify potential threats, document vulnerabilities, evaluate security controls, assign remediation tasks, and track corrective actions. Regular risk analysis is a core requirement of the HIPAA Security Rule.
What is the HIPAA Security Rule?
The HIPAA Security Rule establishes administrative, physical, and technical safeguard requirements for protecting electronic protected health information. It applies to HIPAA covered entities and business associates handling ePHI.
What is the HIPAA Privacy Rule?
The HIPAA Privacy Rule establishes standards for the use and disclosure of protected health information. It also provides individuals with certain rights over their health information, including access and amendment rights.
Can HIPAA compliance software automate employee training?
Yes. Many HIPAA compliance platforms provide training assignments, educational materials, completion tracking, reminders, and documentation. Organizations must still ensure training is appropriate for employees’ responsibilities and applicable requirements.
What is the best HIPAA compliance software for dental practices?
Abyde, Compliancy Group, and Accountable HQ are options for dental practices seeking HIPAA compliance support. Their healthcare-oriented features can assist with staff training, risk assessments, policies, and compliance documentation.
Does HIPAA compliance software help prevent data breaches?
HIPAA compliance software can reduce security risks by identifying weaknesses, tracking corrective actions, and improving oversight. However, it cannot eliminate cyber threats or guarantee protection against unauthorized access and data breaches.
What is a Business Associate Agreement in HIPAA compliance?
A Business Associate Agreement is a contract establishing required safeguards and responsibilities when a business associate handles protected health information on behalf of a covered entity or another business associate.
Can HIPAA compliance software manage Business Associate Agreements?
Some HIPAA compliance platforms support Business Associate Agreement tracking, document storage, renewal reminders, and vendor assessments. These capabilities help organizations maintain oversight of third parties handling protected health information.
How long does HIPAA compliance software implementation take?
Implementation timelines depend on organizational complexity, existing security controls, integrations, and vendor support. Basic configurations may take days or weeks, while enterprise compliance deployments can require several months.
What is the difference between Drata and Vanta for HIPAA compliance?
Drata and Vanta both offer automated compliance workflows, evidence collection, and continuous monitoring. Their differences include integrations, user experience, service packages, pricing, and the depth of support for specific HIPAA requirements.
Is Secureframe suitable for HIPAA compliance management?
Secureframe offers compliance automation, security monitoring, evidence collection, and support for multiple regulatory frameworks. Healthcare organizations should confirm that its HIPAA-specific capabilities match their operational and legal requirements.
What makes Compliancy Group different from other HIPAA compliance platforms?
Compliancy Group focuses specifically on healthcare compliance and provides guided workflows, documentation, training resources, and risk assessment support. Its healthcare specialization distinguishes it from broader security compliance automation platforms.
Is Abyde a good HIPAA compliance solution for small healthcare businesses?
Abyde is designed for healthcare practices seeking streamlined HIPAA compliance management. Its offerings include risk assessment workflows, policy documentation, training resources, and compliance support tailored to smaller organizations.
Can HIPAA compliance software integrate with electronic health record systems?
Some HIPAA compliance platforms integrate with healthcare applications, identity providers, cloud services, and security tools. Direct electronic health record integrations vary by vendor and should be confirmed before purchasing.
What is continuous HIPAA compliance monitoring?
Continuous HIPAA compliance monitoring involves regularly reviewing security controls, identifying configuration changes, tracking risks, and maintaining compliance evidence. Automated platforms can support this process, but human oversight remains essential.
Does HIPAA compliance software help with regulatory audits?
Yes. HIPAA compliance software can organize policies, risk assessments, training records, incident documentation, and remediation evidence. Centralized records can make responding to regulatory inquiries and compliance reviews more efficient.
How should healthcare organizations compare HIPAA compliance software vendors?
Healthcare organizations should compare HIPAA-specific features, pricing, implementation support, integrations, security controls, scalability, vendor reputation, and contractual terms. Demonstrations and compliance requirement assessments can inform selection.
What are the biggest HIPAA compliance software trends in 2026?
Major HIPAA compliance software trends in 2026 include AI-assisted workflows, automated evidence collection, continuous risk monitoring, multi-framework compliance management, improved vendor oversight, and stronger integration with healthcare security systems.